
Every alert investigated. Detection coverage perfected.
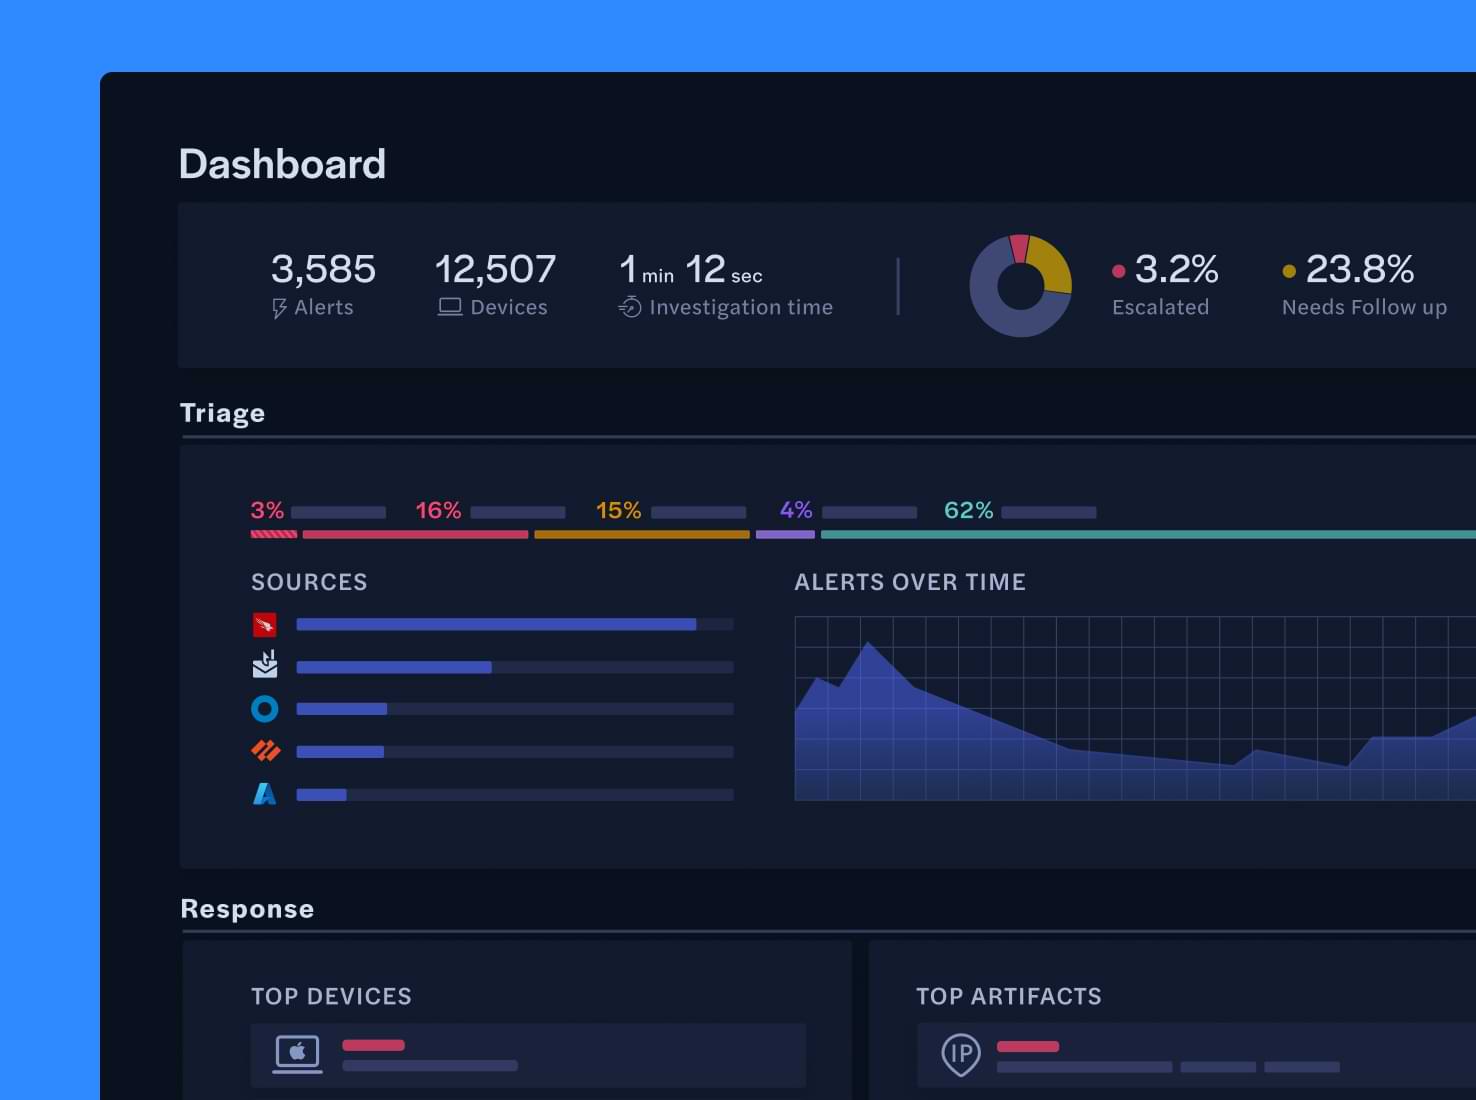
Intezer AI SOC investigates every alert at forensic depth so your team can focus on real threats, while investigation outcomes continuously improve detection coverage.
Focus on what matters with 24/7 coverage you can trust
Intezer AI SOC combines proven forensic capabilities, including endpoint forensics, reverse engineering, network artifact analysis, and sandboxing, with agentic AI reasoning. The result is sub-minute triage across 100% of alerts, with fewer than 2% escalated and 98% verdict accuracy, all with full transparency.
Monitor and remediate endpoint alerts 24/7
Integrate with CrowdStrike, SentinelOne, and Microsoft Defender in seconds.
Intezer automatically collects and analyzes files, logs, command lines, memory images, and more to resolve false positives and escalate real threats with recommended actions for review or automated remediation.
Automatically investigate identity-related alerts
Accurately triage Entra ID, Okta, JumpCloud and other IDP alerts to reduce MTTR. Intezer queries IDP data, reviews findings against threat intelligence, contacts users for feedback, as well as proposes and executes the next steps.

Resolve user-reported phishing with confidence
Eliminate manual review of abuse mailboxes.
Intezer connects to Office 365, Proofpoint and similar tools to handle triage automatically. It parses raw email data, scans attachments, and analyzes URLs to detect common phishing tactics and return a clear verdict with priority, classification, and context. Only alerts that need a human actually reach one.

Analyze and prioritize network alerts
Seamlessly connect into your entire security stack and network.
Intezer deeply analyzes IPs, URLs, correlates alerts to identify patterns, reviews environment context and take action, resolving false positives, auto-remediating where relevant and escalating real threats.

Triage cloud alerts
Keep your cloud assets secure with deep integrations into your SIEM, workload protection solutions, or tools like Wiz. Investigate alerts with full context from logs and connected data sources. Perform in-depth analysis to understand the scope of any threat. Get detailed recommendations on remediation steps and automatically resolve false positives.

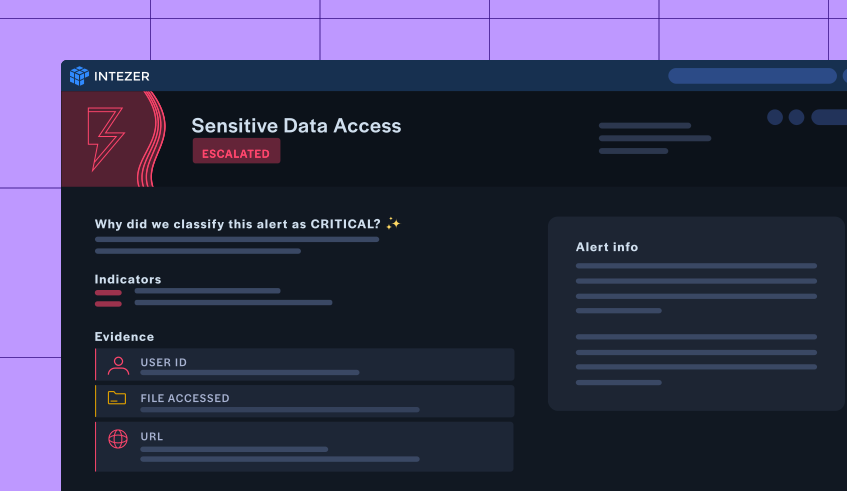
Investigate DLP alerts
Ingest data loss alerts straight from your SIEM or tools like Wiz. Intezer assesses each alert against the identity behind it, checking whether the access matches that person's role, permission level, and normal behavior. Routine activity gets resolved automatically, and real risk is escalated with recommended remediation steps.
The complete AI SOC operating model
Intezer AI SOC combines agentic AI with deterministic forensic analysis to investigate every alert at expert depth and machine scale. Every verdict sharpens detection engineering and organizational knowledge, while custom agents and workflows put automation and response in your hands without a separate SOAR. Intezer experts remain on call for the most complex incidents.
Zoom in or click to see more.

Integrations that go beyond the surface
Our native integrations are built for the depth and rigor of the triage and forensic investigation process, providing robust, full-featured connections between tools. This allows Intezer to ingest alerts from all major sources within seconds, gather richer evidence, and deliver deeper context in every analysis. Remediation actions can be easily automated with explicit human approval.








Expect more from your AI SOC
The modern SOC needs more than AI alone can offer. Intezer pairs AI flexibility with deterministic, forensic guardrails, along with on-demand expert access, and predictable, endpoint-based pricing, so security teams can scale without compromise.

Accurate, fast triage, 24/7/365
Regardless of alert volume, Intezer delivers consistent, lightning fast and in-depth triage and investigation. Every alert, including low-severity ones, receives the same rigorous level of scrutiny, reducing unnecessary escalations and ensuring your team catches threats that human-only teams will miss.
Forensics built-in
Intezer AI SOC incorporates advanced forensic capabilities, from automated evidence collection via EDR/SIEM/IDP to memory analysis, reverse engineering, network artifact forensics, and sandboxing. This enables sub-minute, scalable triage for all alerts, including low-severity ones often abused by attackers.

Keeps humans in the loop
With transparent triage logic, clear explanations, and the ability for analysts to review or override escalated alerts, Intezer keeps humans in the loop. Intezer AI SOC continuously improves through user feedback and in-house QA with ongoing self-testing and benchmarking. Combined with 24/7 access to our expert analysts, Intezer is a genuine security partner.

Scalable and predictable pricing
Intezer's unique architecture combines deterministic analysis with efficient AI models to triage most alerts without resource-intensive LLM processing. This delivers native scalability and stable, predictable pricing tied to organizational size, such as number of endpoints, so you get enterprise-grade performance without unpredictable cost spikes.

Hear from our customers
hospitality
The results from Intezer's Al-driven alert triage are amazing and transformative for security operations.
Branden Newman
CTO, MGM RESORTS INTERNATIONAL
manufacturing
The more information that we have from Intezer, the faster a human can make a decision about what to do. If we were to hire the staff needed to respond at this scale, the cost could have been significantly higher.
Michael Calderin
CISO, YAGEO GROUP
Software
Intezer is well integrated into our SOC team’s daily workflows. It's all automated. Our analysts now have time for more proactive security.
Matan Ziv
Lead Incident Responder - CSIRT, SALESFORCE
MSSP
By automating triage and providing us with enriched threat intelligence, Intezer empowers us to focus on high-priority incidents and take decisive action to protect our clients.
Todd Willoughby
Director, RSM DEFENSE
RETAIL
In terms of IT security, Intezer definitely increases our efficiency. We are saving time. In terms of risk, we can react faster.
Piotr Albrecht
Security Officer, DPD POLAND
Empower your SOC with more
With Intezer, you give your SOC team more. More trust that you're catching dangerous threats with comprehensive investigation of every alert, even low-severity ones. More time for your human analysts to tackle proactive security initiatives instead of chasing false positives. More scale to triage growing alert volumes cost-effectively.

Find threats in your low-severity alerts
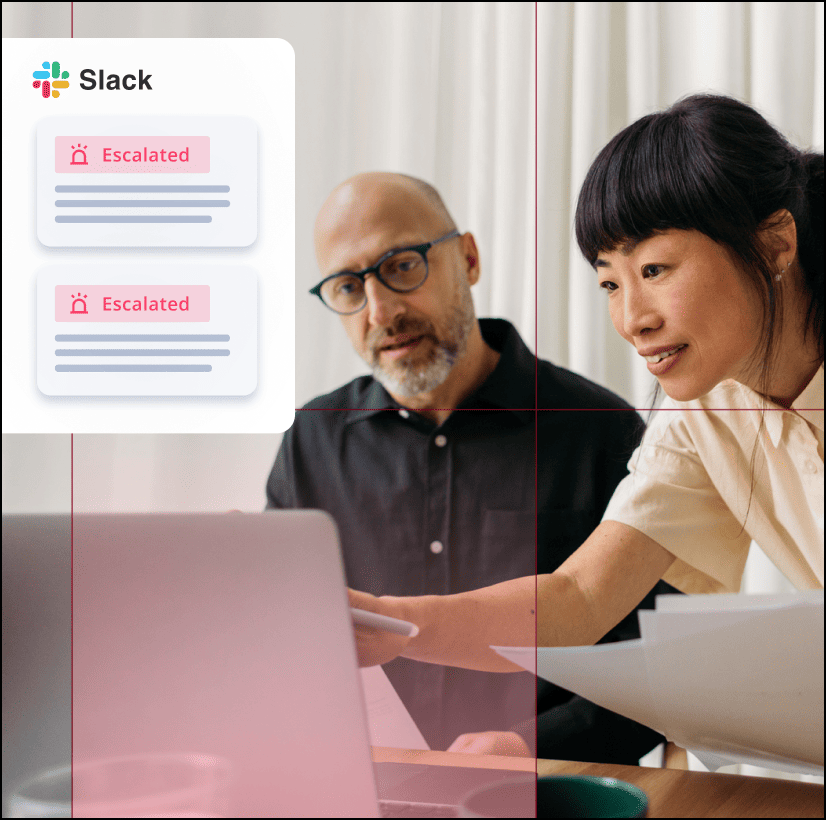
Intezer thoroughly investigates every alert in minutes. Instead of "accepting" the risk hidden in your unreviewed low-severity alerts, you can rest easy knowing that every alert will be fully analyzed, every time.

Reevaluate your MDR and scale capacity efficiently
With fewer escalations and higher accuracy, SOC managers can refine resource allocation by reviewing their MDR contract or expanding endpoints under management, without growing their team.

Grow your team’s potential
With Intezer taking on primary triage duties, your team can now tackle more strategic security initiatives, driving meaningful impact to your security posture.

Frequently asked questions
Intezer AI SOC investigates every alert your security tools raise, including low-severity ones, and returns a verdict in under a minute. For each alert it collects the evidence a human analyst would ask for, then analyzes it with deterministic forensics alongside proprietary and commercial AI models, spanning correlation, sandboxing, reverse engineering, script analysis and live memory forensics. Over 98% of false positives are closed automatically, fewer than 2% of alerts are escalated to a human, and verdict accuracy is 98%. Every verdict can be challenged in the platform, and your feedback tunes both the triage logic and the detection rules to your environment.
Intezer has over 100 native, bi-directional integrations. On endpoint it connects to CrowdStrike, SentinelOne and Microsoft Defender. On identity it connects to Entra ID, Okta and JumpCloud. For reported phishing it connects to Office 365 and Proofpoint. On cloud it works with tools such as Wiz, and it ingests from major SIEMs including Splunk and Microsoft Sentinel alongside asset management, ticketing and SOAR platforms. Connecting a tool takes a few minutes with an API key, and triage results appear in your dashboard within the hour.
While MDR is a proven model in which the provider's analysts investigate alerts on your behalf, depth and coverage are bounded by analyst availability and the contract, and low-severity alerts are often deprioritized. Intezer investigates 100% of alerts at forensic depth, including low-severity ones, escalates fewer than 2% to a human, and keeps every verdict transparent and challengeable by your own team. A SOAR automates steps a human already decided on and requires playbooks to build and maintain. Intezer automates the investigation decision itself, collecting evidence, analyzing it and reaching a verdict, with custom response workflows and actions triggered according to your policy. For teams that have outgrown a human-scaled model, Intezer is the natural next step.
The primary onboarding tasks are connecting your alert sources and then adding members of your team as new users to your Intezer account.
It takes a few minutes to connect a security tool as a new alert source in Intezer, using an API key with the necessary permissions. After adding your API key to Intezer, you should start seeing alert triage results in your dashboard within the hour.
More than 150 enterprises use Intezer, including Equifax, MGM Resorts International, NVIDIA, Salesforce and other Fortune 500 security teams, to investigate and remediate the high volume of their security alerts. Customers span every vertical, serving large enterprise SOCs and MSSPs.

Experience Intezer
Discover how AI-powered alert triage and investigation can supercharge your SOC's efficiency.