
In cybersecurity, initial alert triage is like detective work. It demands quick, detailed, and accurate analysis to separate real threats from false positives. But most Security Operations Centers (SOCs) face overwhelming challenges including skyrocketing alert volumes, resource shortages, and limited time for investigations.
At Intezer, we’ve reimagined the triage process by bringing reverse engineering (RE)—a skill traditionally reserved for senior analysts—right to the front of your alert pipeline. Our AI-driven approach empowers your Tier 1 SOC team to leverage expert-level analysis from the outset, transforming how alerts are triaged.
Reverse Engineering for Your Tier 1 SOC
What is Reverse Engineering?
Reverse engineering is the cornerstone of advanced threat analysis and one of the most specialized skills in cybersecurity. It involves deconstructing files, software, or malware to understand their behavior and assess risk. However, this critical expertise is rare and not something that can be learned quickly or easily.
Why is Reverse Engineering Important?
Traditional triage and analysis often prioritize speed at the expense of accuracy and only provide surface-level insights. This approach can lead to missed context, incomplete investigations, and unnecessary escalations.
On the other hand, reverse engineering goes much deeper. It reveals the true capabilities of malware—even when it employs advanced sandbox evasion techniques, relies on external dependencies, or has environment-specific requirements.
Intezer’s Autonomous SOC platform was designed to bridge this gap. By integrating reverse engineering principles at the Tier 1 level, Intezer’s AI is able to automate this deeper analysis, offering organizations insights that no other tools or experienced human analysts can achieve.
Powerful Insights From Powerful AI
The Intezer Autonomous SOC is more than just a pretty UI with some basic OpenAI prompt engineering tacked on. Its power lies in the sophistication of our AI, which enables these deep insights through advanced reverse engineering.
At the heart of our platform is a unique Genetic Analysis that identifies reused code or patterns at the binary level. This allows us to accurately attribute malware to specific families and threat actors, delivering a superior level of precision.
By automating complex processes like memory forensics and deep endpoint inspection, Intezer's Autonomous SOC eliminates the need for resource-intensive, human-led workflows.
Additional benefits includes:
- Immediate Triage: Manual reverse engineering can take hours (or even days) to analyze a single alert. Intezer’s platform achieves the same depth of analysis in seconds, filtering out 97% of false positives, and enabling teams to focus on the alerts that demand their attention.
- Consistent, High Quality Investigations: Our technology ensures every alert receives the same meticulous level of analysis, eliminating inconsistencies. In fact, Intezer’s Autonomous SOC identified 60% of confirmed threats other detection systems had misclassified as low or medium severity.
- Quick Time to Value: Intezer integrates seamlessly into your existing workflows in minutes, requiring no engineering resources for setup. It then delivers actionable results directly to your EDR, SOAR, email, or ticketing system.
Supercharge Your SOC with Intezer
Intezer’s Autonomous SOC doesn’t just automate alert triage, it revolutionizes the process by democratizing advanced tools and embedding reverse engineering into the heart of your Tier 1 operations.
Our advanced AI surpasses the capabilities of even the most seasoned analyst, maximizing your team’s efficiency and accuracy.
Free your analysts from the noise and let them focus on the strategic, high-value initiatives that matter most to your organization.
Ready to transform your SOC? Learn more about Intezer’s Reverse Engineering Capabilities. Sign up for a demo today!

Jim McDonough
Jim has spent the past 17 years working in fast-growing SaaS companies. He was the VP of Revenue, most recently responsible for sales and customer success at Threat Stack, where he spent five years. Outside of work, Jim is the Vice-Chairman of Board of Directors for the non-profit Boston Uncornered.
In this article
Share article
Related Articles
Alert Triage
AI SOC
3 min
We let a fruit fly brain triage 12,716 real SOC Alerts. Here is what happened.
On behalf of people who run SOCs, we explore how a fly brain triages alerts compared with a boring linear model you could train in eleven seconds.
AI SOC
4 min
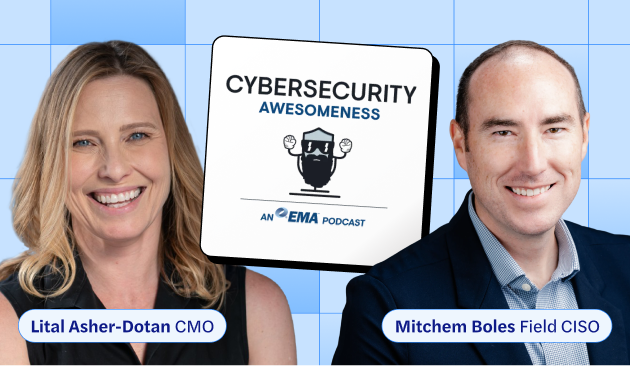
The impact of the AI SOC: Intezer joins the Cybersecurity Awesomeness Podcast
Intezer's Field CISO and CMO join the Cybersecurity Awesomeness Podcast to explain what the AI SOC is, how it cuts false positives, and why analysts end up more empowered.
AI SOC
CISO
MDR
4 min
Financial services need to rethink the MDR model
MDR providers investigate only about 40% of alerts. Learn why financial institutions are rethinking MDR renewals and what full alert coverage requires in 2026.