The impact of the AI SOC: Intezer joins the Cybersecurity Awesomeness Podcast
September 14, 2026
An AI SOC uses agentic AI together with deterministic forensic tools to automatically triage, investigate, and escalate security alerts at the depth of a tier three analyst, so human teams can focus on the incidents that actually matter.
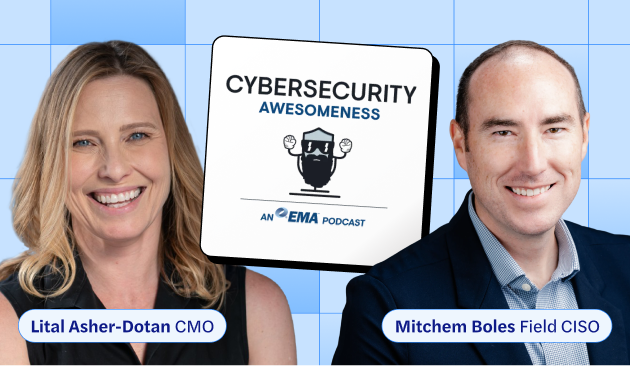
What does the AI SOC actually change for security teams, and why is everyone from Black Hat to the boardroom talking about it? Intezer's Field CISO Mitchem Boles and CMO Lital Asher-Dotan joined Chris Steffen on the Cybersecurity Awesomeness Podcast to dig into how AI is reshaping security operations. They cover how agentic AI differs from traditional SOC automation, why combining deterministic forensic tools with AI reasoning cuts through false positives, what it takes to build trust in autonomous triage, and why analysts who hand off tier one grunt work end up more empowered rather than replaced. The conversation wraps with a look at what security leadership might look like three to five years from now, when AI executes and humans supervise.
Key takeaways
- An AI SOC automatically triages and deeply investigates every alert coming from EDR, phishing, cloud, and other sensors, applying the forensic depth that previously only a tier three analyst could deliver.
- Combining deterministic forensic tools with security-specific AI reasoning is what cuts false positives, pairing repeatable evidence with contextual judgment across code, behavior, and semantics.
- SOC teams face tens of thousands and sometimes hundreds of thousands of alerts, and real attacks can hide inside alerts an EDR never marks as severe, which is why 100% alert coverage matters.
- Analysts who hand off tier one grunt work report feeling more empowered, shifting from repetitive triage to orchestrating response, planning, and strategy.
- The operating model for the next three to five years is simple. AI executes. Humans supervise.
Listen to the full episode here, or read the transcript below.
Cybersecurity Awesomeness Podcast episode 170 transcript
Chris: Good morning, good afternoon, good evening. Welcome to the cybersecurity awesomeness podcast. I am your host. My name is Chris Steffen. Joining me today, I have some friends from Intezer, I think is how you pronounce the name of the company. We are going to be talking about AI SOC. And it is something that of course if you were at Black Hat just recently, everybody was talking about it there. We've been talking about it actually for some time now. What are the benefits? Is this something that I can actually trust the keys of the kingdom to? Is this coming for my job? I know that we keep on having the conversation about AI destroying the workforce and come on give me a break. It's not, I promise you my friends here will be able to talk a little bit more about that. But again, I think it's really important to understand some of the fundamentals of what the AI SOC is, what it's going to be doing for our security operations and how it is really going to kind of change how we look at security operations in general. So with that enough introduction, Mitchem, why don't you go ahead and introduce yourself and then Lital you can take and go after that.
Mitchem: Absolutely phenomenal to be here. I'm Mitchem Boles. I serve as a field CISO for Intezer
Lital: and hi Chris. Pleasure to be here. I'm Lital and I'm chief marketing officer at Intezer. Very excited to talk about those changes in the world of AI SOC.
How is the AI SOC different from traditional SOC automation?
Chris: Again, really appreciate you both here. It is going to be a great conversation. One of the very first questions that I wanted to ask both of you, and both of you can kind of choose. I look at cybersecurity as this constant evolution. We've been doing things on the bleeding edge for a long time from again, you're talking about the original firewall monkey. I used to take and do and look at allows and denies to the SIEM taking and bringing some amount of automation to great automating playbooks to a tool set that is so vast that you can't possibly understand every feature. And the question really that I think a lot of people are asking is how is this AI SOC innovation? How is it different than the traditional automation and what problem do we think that it's really solving that some of these old tools that I've been using since like the beginning of dirt? How is it solving things that I wasn't able to solve before?
Lital: Great question, Chris. I think that like everything in security, it's all evolution. It's the next step. And at the SOC, you have great tools doing detection on the network level, on email, on endpoint, cloud. You have those sensors that were developed across the years together with the threats that were involved and with the technology and are now really tuned in to detecting threats and alerting us on specific behaviors. What didn't change yet is what you exactly said. Your role was the people watching those tools, looking at those alerts, making decisions, making the verdicts. And they had some capabilities and unique capabilities depending on what level they were. And we are now bringing in this ability to automatically take all the alerts that's coming from all the great sensing tools that we have in the SOC, EDR, phishing, cloud, etc. triage all the alerts deeply investigate them at the forensic level using some deep forensic tools that have been used for many years developed across the years bringing external threat context and then make precise verdicts of those incidents that matter, escalate them for human being decision. So that's the great advantage of what we have today that we can handle all those tens of thousands and sometimes hundreds of thousands in alerts and give them the treatment that only a tier three analyst would be able to give them the forensic level treatment so that we focus on what actually matters and we can finally talk about risk reduction for the organization.
How does AI reasoning plus deterministic forensics reduce false positives?
Chris: Yeah, I love that answer. And I want to take it to the next step further. I wanted to talk specifically about one of the big differences in AI is that it doesn't just read the logs. It doesn't just take and do in some kind of like low level whatever and do a network trace or whatever it's going to end up doing. It actually takes and does a whole bunch of combinations and taking these technical forensics and uses a certain amount of reasoning that actually helps eliminate false positives instead of just kind of shuffling around. And then you actually get a better picture of how an attack is going on. Talk to me a little bit about that. I know that that's kind of the future of what AI SOC is going to look like. Talk to me about are we seeing that today? Are your customers seeing that today? Is that something that we should be expecting in the future?
Mitchem: I think this is an excellent question. I think that part of the problem actually is still identified as tokenomics. Like being able to do the reasoning, being able to utilize different AI models at whatever sophistication level they are can input or interpret different results as the outcome. And so I think there are actually a couple of things that the industry has almost shied away from is talking about deterministic tools for forensic tools that actually give you those outputs that you are expecting and need to be repeatable and need to look at things that no one else is going to look at at that scale. That's where the industry's baseline needs to be right now. But there is no doubt that AI has been able to be a massive indicator of a lot of different combinations like you mentioned looking at behavioral analysis, for instance, or something that takes a lot of different inputs and takes the semantics of what text was looked at and not just a URL analysis and sub analysis and all these different things that have to look at, hey, what was the code there? We've never seen this code before. Is it actually malicious or not? And so being able to have forensic tools to lean on to do that and in the midst of that and interwoven having security specific AI, LLMs looking and reasoning across these different things give an incredible output of validation, of accuracy. And it's that combination that I think takes everyone much, much further. But no doubt that also in the flip side of that, the baseline has to be a reduction in false positives because it has to be getting rid of the noise and being able to get directly to the signal.
How do teams build trust in autonomous triage?
Chris: Yeah, I totally agree with that. One of the things that I think brings promise with the idea of an AI SOC is that at the 100,000 foot, a tier one analyst gains tier two strength and they do so by really looking at the things that actually matter instead of looking at things that are dumb. Right. And so I think we're going to continue seeing that evolution as we gain more trust with the agentic solutions, so on and so forth. I want to talk a little bit about how when you look at AI SOCs, agentic solutions, agentic AI, how it really kind of flips how the math works in the SOC. You go from a workflow where a human is forced tier one, tier two, tier three is required to handle a vast majority. I mean, even automation takes care of some, but a vast majority of those concerns are still have to be handled by a human. But now all of a sudden you decrease that workload. It isn't that we're getting rid of those analysts, but those analysts are actually taking and doing things that need to have some kind of human intervention. And that is a really cool thing to me. Talk to me a little bit about that. Talk to me about how do you build that trust in an AI SOC solution that the agentic solution can handle a lot of those tier one concerns, allowing the humans to concentrate on bigger picture more important types of things.
Lital: I think once the human beings in the SOC have strong belief in the outcomes that they see coming out of an AI SOC platform and the ability to cover all those alerts that weren't handled before, they see themselves as upscaling only, you know, doing the high level work of what actually matters, which is securing the organizations, dealing with those incidents that need to be taken care of.
Is AI coming for SOC analyst jobs?
Chris: That's right. I want to be really clear about that too. So you're focusing on the point that I really, really want to talk about and that is you hear a lot of fear and questions about, well, we're going to eliminate a whole bunch of members of the SOC because AI can do that. And you hear that in the most or more general phase all over the place. We're going to get rid of people because AI is going to take over the workload. We're obviously finding out daily how much of a mistake that idea even is specifically with the SOC. Trust me when I tell you and I speak from personal experience, you do not want to be doing the tasks that you can hand off to a trusted automated device. You don't want to be looking at allows and denies in a firewall. Why it stinks, I promise you. I promise you because I was the guy that had to do it so I can tell you emphatically it sucks. If I can hand that over to an AI SOC absolutely I'm going to do that. So I want again your point is great and I want to emphasize that point because it's critically important.
Mitchem: Well, no doubt. And I think, you know, I had my career in SOCs and then being able to lead security programs that had SOCs and then consulting for organizations that indeed had security operations. And we just have been doing all this garbage work for so long that didn't mean anything, giving value to the human criticality of the context awareness, what's specific to that organization like jumping into that is such a value differentiator for the team and the people that are leading or being in the SOC. That is such a massive shift from where it was before. And that's probably one of the most exciting things to come out of this. Not to mention if you get to look at, you know, excuse the analogy, but looking at just the needles in the haystack instead of having to look through all the haystack, all of a sudden you find the real things that matter and you become much more potent and powerful as an analyst to be able to get to the outcomes of securing the organization or responding quickly when something is there. And so now you're talking a matter of minutes instead of hours or days or even longer.
Can defenders respond at the speed of AI attackers?
Chris: Well one of the questions that people ask all the time and it's totally relevant to what you were just saying is that can we actually respond at the speed of AI? And the answer is no, right? I mean, you can be the greatest SOC analyst of all time and you still can't defeat a thousand person AI bot army. You can't do it. You just don't have the absolute capacity. Your fingers don't move that fast if nothing else. Right. And so are we looking at a time where that SOC analyst becomes the general of their agentic SOC solution team to defend themselves against the AI bad guys? Because again, let's be clear, the bad guys are taking and using AI. They're going to continue using AI. And so I think it's critically important that we understand that we need to also be embracing AI because the bad guys are coming after us with it no matter what we want to do with it. So keeping that in mind, do you see that AI arms race kind of really kind of shaking out that way? Do you see that the bad guys are continuing to use AI and it's important to respond with having an AI SOC solution to basically help you defend your infrastructure?
Lital: Absolutely in the world of, you know, Mythos [the frontier AI model that made the news with concern that attackers would be unstoppable with it], exploitation and AI generated attacks and everything. Of course, the speed, the robustness, the ability to look at all alerts generated because real attacks might be hidden into, you know, in those alerts that are not necessarily marked at severe alert by your EDR in this world. Yes, you have to have the ability to respond as fast as possible, if not automatically. So being able to do the auto triage auto investigate and then have the human beings build automatically built in an easy way, what would be the response in case of an XYZ and automate that, automate the ability to isolate host when needed, you know, send a new password to a user. This is really important us thinking about those use cases and building the ability to autorespond while also letting us have the freedom to make things not autonomous when human beings are needed. And if I can say, Chris, what are we seeing from the human beings in the SOC? They feel empowered. They feel the ability to now take over and not outsource some of the work that was outsourced for them. So they don't feel like the job is being taken. Like you just said, they now feel like they're moving into more orchestrating the ideal response in case of. They can plan now. They can take a breath of fresh air and strategize.
What does security leadership look like in three to five years?
Chris: Yeah, I totally agree. And I, again, I've talked about this plenty of times and I don't know who keeps on writing about the AI is coming for your job. And I'm sure it's coming for some I am not trying to dismiss that. But you go talk to the SOC people that are taking in and deploying agentic solutions and automated solutions. And they ain't worried. Okay. They realize what their value is and they realize what the value of this tool is. We're almost out of time. I wanted to very quickly give you guys a chance to talk about this. I am, as we were just discussing, I want to understand what the security leader is going to look like in three to five years. Are we managing bot armies? Are we back to only humans in the SOC? Are we some kind of field general? I really kind of want to understand what you kind of think that picture looks like when it's all said and done.
Mitchem: I think a quick nomenclature here could be that AI executes and human supervise. I think that it massively enriches everything that people are doing. They're able to steer. They're able to review. They're able to place context that has not gatherable based on just technology and tools that it's actually something that's in the human brain. There are other things that matter about taking a production server down that is where all the money is being made for that company and making that decision instead of making it lightly or autonomously that they are still incredibly valuable for that. So then the security leadership is then generating this opportunity for leading a strategic move into how to consolidate integrations across the entire organization, how to gather context in the right way, how to be able to massively empower their teams to go do that. And I do think that it is human centric, but it has to come with the tools that actually will scale to fight back on and defend and do the things that we've always and maybe even nominally gotten tools to do in our past for cybersecurity. And so security, I think, will continue to actually blossom as it both consolidates platforms and finds new niches to actually go after and make sure that individual organizations are protected. So I think it has many different legs of that to make sure that it can be implemented well. But it's a huge role for the future in three to five years just as it has been, but even more so going forward.
Chris: Yeah, I couldn't agree with you more. There is so much evolution and it literally evolves on a daily basis. So Lital, Mitchem, thanks for coming on the podcast. Your insights are great. We can obviously be talking about this for the next 16 hours. I'm really glad that we did, we're able to take and have this conversation today. If you are listening to this podcast and you're looking for more information about Intezer, intezer.com, they will be happy to take and provide that additional information. I promise you we're not done talking about AI. I know it seems like I say this every week. We're going to continue talking about AI. We're going to continue talking about AI SOC. I think it's a critical path. But I hope this has been interesting to you. And until next time, thanks for listening.
Intezer
Count on Intezer AI SOC to triage, investigate and respond to every alert at unmatched speed and accuracy.
In this article
Share article
Related Articles
AI SOC
4 min
The impact of the AI SOC: Intezer joins the Cybersecurity Awesomeness Podcast
Intezer's Field CISO and CMO join the Cybersecurity Awesomeness Podcast to explain what the AI SOC is, how it cuts false positives, and why analysts end up more empowered.
AI SOC
CISO
MDR
4 min
Financial services need to rethink the MDR model
MDR providers investigate only about 40% of alerts. Learn why financial institutions are rethinking MDR renewals and what full alert coverage requires in 2026.
AI SOC
3 min
Analyst firm SACR recognizes Intezer in the AI SOC category
What makes an AI SOC trustworthy? SACR's 2026 research points to evidence, context and verified action. See how Intezer was evaluated.