
Explore our blog
AI SOC
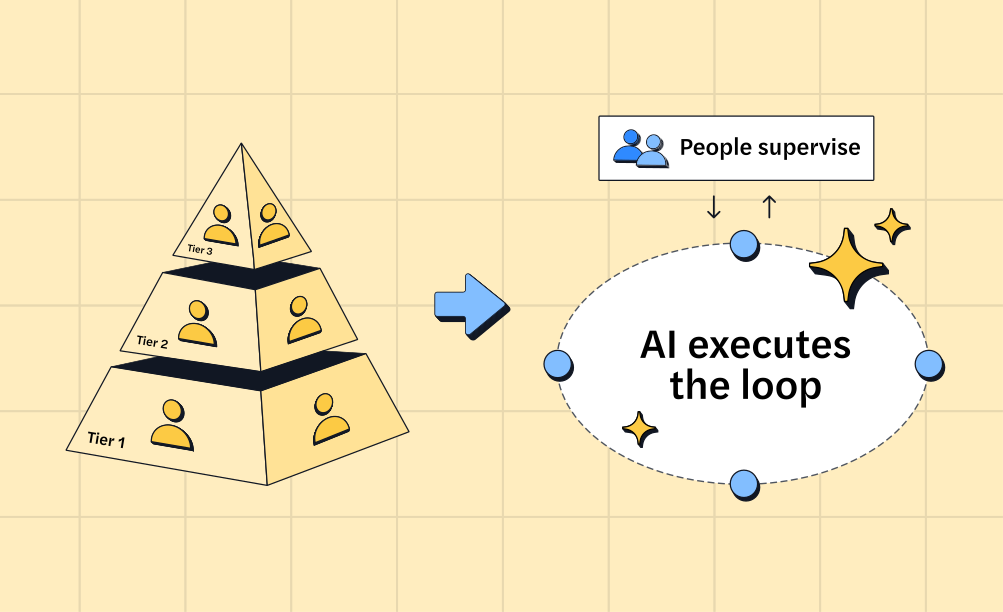
The end of the SOC pyramid
AI is retiring the SOC pyramid. Learn how a tierless AI SOC investigates 100% of alerts with forensic evidence while your analysts supervise outcomes.
Zev Schonberg
Research
5 min
NinjaMare and the enterprise security epidemic hiding behind a harmless label
The PUA label, aka "potentially unwanted application" means nuisance. Adware, toolbars, and other things that change your settings without asking. Our research team's findings say this label is far more serious than a mere nuisance.
Intezer
View Topics

Incident Response
4 minutes
Revealing the Origins of Software with Genetic Analysis
By revealing the origins of software, the Genetic Analysis approach can detect in-memory threats designed by attackers to not generate noise.
Incident Response
2 minutes
Genetic Malware Analysis for Golang
Intezer Analyze now supports genetic analysis for files created with the Golang programming language. Users can detect and classify malware written in Go, within seconds!
Research
8 minutes
ACBackdoor: Analysis of a New Multiplatform Backdoor
ACBackdoor is a multiplatform backdoor with Linux and Windows variants. The malware lacks known connections to other threat groups, which may indicate the retooling of a known threat group or the formation of a new one.
Research
8 minutes
PureLocker: New Ransomware-as-a-Service Being Used in Targeted Attacks Against Servers
Researchers at Intezer and IBM X-Force have identified a new, undetected ransomware threat being used in targeted attacks against enterprise production servers and databases.
Threat Hunting
3 minutes
Intezer Analyze Community Halloween Edition: Trickbot or Treat!
In the spirit of Halloween we’re spotlighting three “spooky” threats detected by the Intezer Analyze community in October. And as a special treat, we’re giving away three code-based YARA signatures which can be used to hunt for additional variants of these threats!
Incident Response
2 minutes
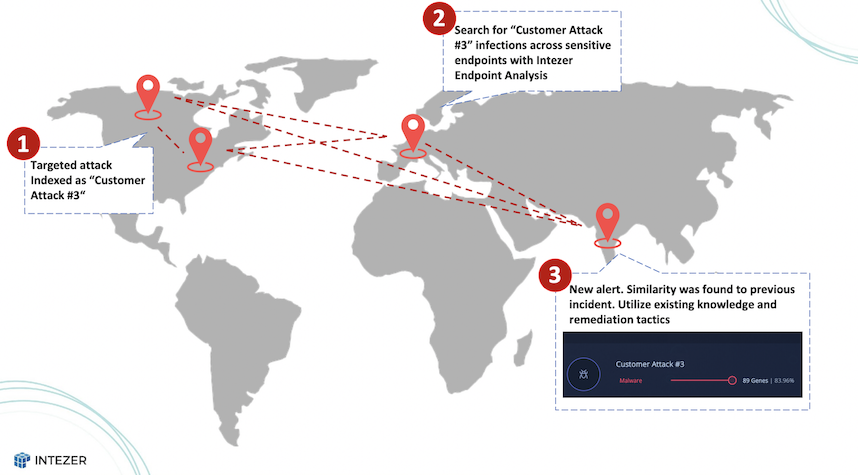
Intezer Analyze Use Case: Visibility Among Global SOCs
SOCs from the same organization can leverage Intezer Analyze to automatically share classifications and remediation tactics on previous incidents.
Research
19 minutes
Mapping the Connections Inside Russia's APT Ecosystem
Research conducted in a joint effort between Intezer and Check Point Research maps the Russian APT ecosystem on an unprecedented scale.
Research
3 minutes
Russian Cybercrime Group FullofDeep Behind QNAPCrypt Ransomware Campaigns
We can assess with high confidence that FullofDeep, a Russian cybercrime group specializing in ransomware operations, is behind both the original QNAPCrypt campaigns and the newly identified ransomware variant.
Incident Response
8 minutes
Why we Should be Paying More Attention to Linux Threats
By applying a Genetic Malware Analysis approach, and adhering to the mitigation recommendations outlined in this blog, users of Linux-based systems—particularly organizations hosting their data on Linux cloud servers—can better protect themselves from the threats posed by this emerging landscape.
Research
1 minute
MoP - "Master of Puppets" - Advanced malware tracking framework revealed at BlackHat Arsenal 2019.
At BlackHat Arsenal 2019 Intezer’s researcher, Omri Ben-Bassat, revealed open-source tool called MoP (“Master of Puppets”) which is a framework for reverse engineers who wish to create and operate trackers for new malware found in the wild for research purposes.

Malware Analysis
4 minutes
Intezer Analyze Community: GonnaCry, HawkEye, BXAQ and More
In July, Intezer Analyze community users detected GonnaCry ransomware, the HawkEye malware kit, and BXAQ, the spyware the Chinese authorities have been installing onto foreign travelers’ Android devices.
Malware Analysis
3 minutes
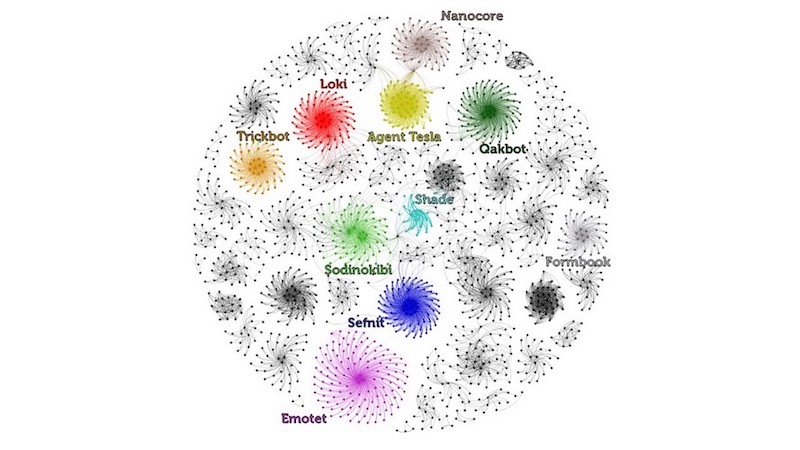
Intezer Analyze Community: Mapping Code Connections Between Malware Samples
Studying genetic connections between malware samples and families detected and classified by the Intezer Analyze community.

Research
8 minutes
Watching the WatchBog: New BlueKeep Scanner and Linux Exploits
Researchers have discovered a new version of WatchBog, a cryptocurrency-mining botnet operational since November 2018. It is estimated that 4,500 Linux machines have been infected by this new malware campaign since June 2019.
Research
8 minutes
EvilGnome: Rare Malware Spying on Linux Desktop Users
EvilGnome, a rare type of malware with zero detections in VirusTotal, is spying on Linux desktop users by allowing the recording of audio conversations. The malware has infrastructure connections to Russian APT Gamaredon Group.
Research
11 minutes
How We Seized 15 Active Ransomware Campaigns Targeting Linux File Storage Servers
Researchers at Intezer have detected and temporarily DoS’d the operation of a ransomware targeting Linux-based file storage systems. It can be assessed with high confidence that this malware, named QNAPCrypt, was developed by the authors of Linux.Rex.