
Explore our blog
AI SOC
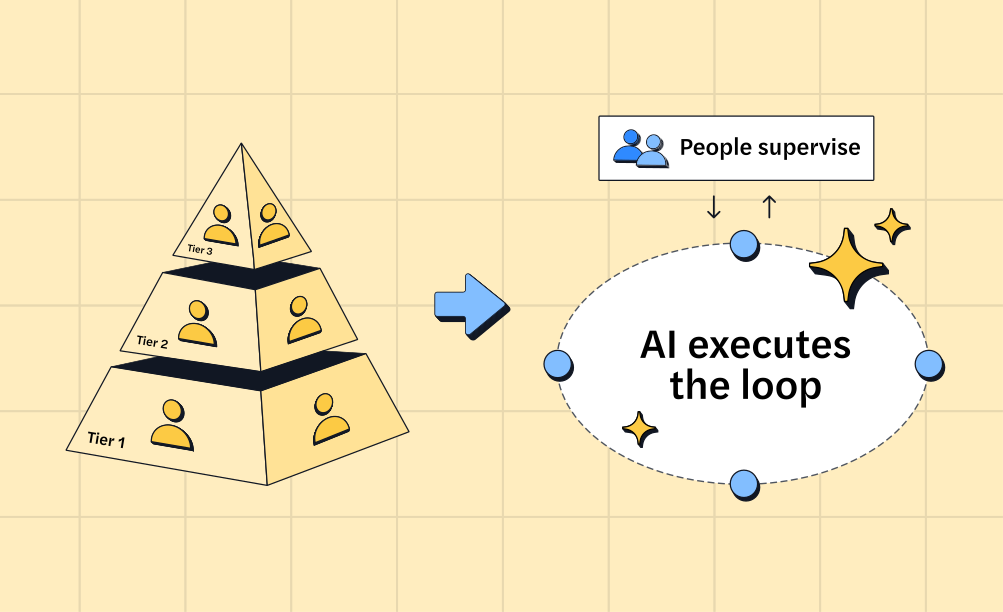
The end of the SOC pyramid
AI is retiring the SOC pyramid. Learn how a tierless AI SOC investigates 100% of alerts with forensic evidence while your analysts supervise outcomes.
Zev Schonberg
Research
5 min
NinjaMare and the enterprise security epidemic hiding behind a harmless label
The PUA label, aka "potentially unwanted application" means nuisance. Adware, toolbars, and other things that change your settings without asking. Our research team's findings say this label is far more serious than a mere nuisance.
Intezer
View Topics
Cloud Security
4 minutes
Pre-runtime vulnerability scans or runtime protection: Which is better for your IaaS security?
Under Armour’s famous slogan sums up the mission perfectly: We Must Protect this House. But how do security teams protect their Infrastructure as a Service (IaaS) while acknowledging the cloud has unique performance needs?
Research
2 minutes
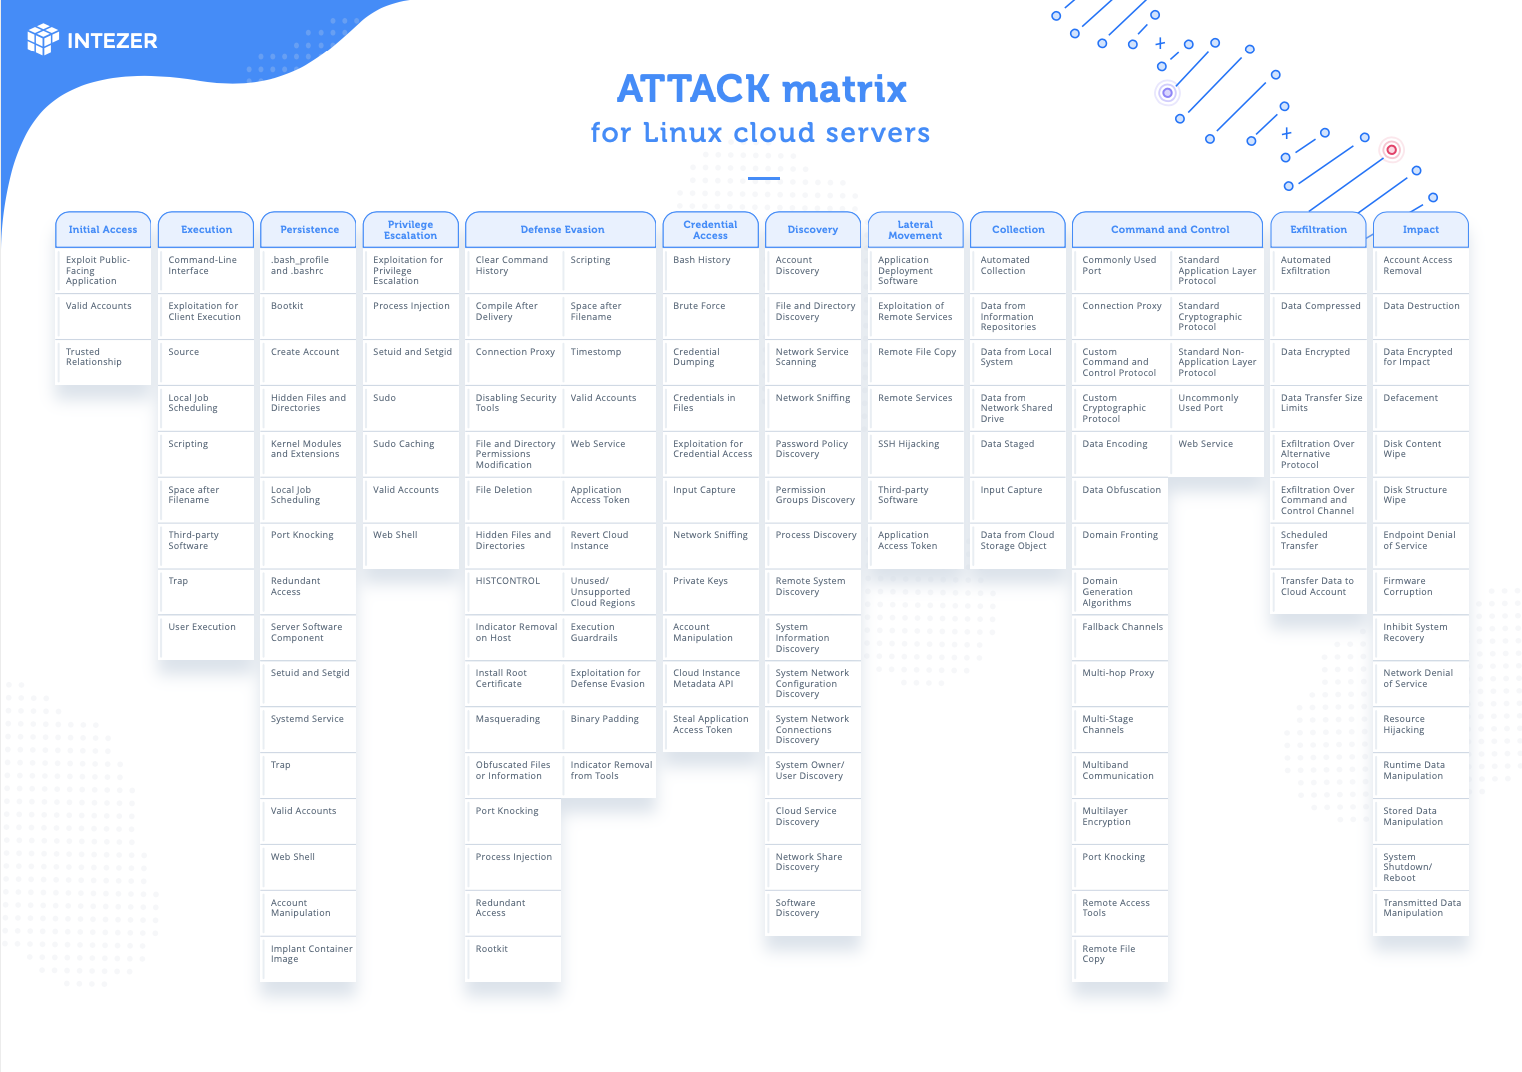
TTPs matrix for Linux cloud servers
Taking inspiration from the MITRE ATT&CK® framework, we have developed a matrix categorizing adversary tactics and techniques for Linux cloud servers.
Incident Response
2 minutes
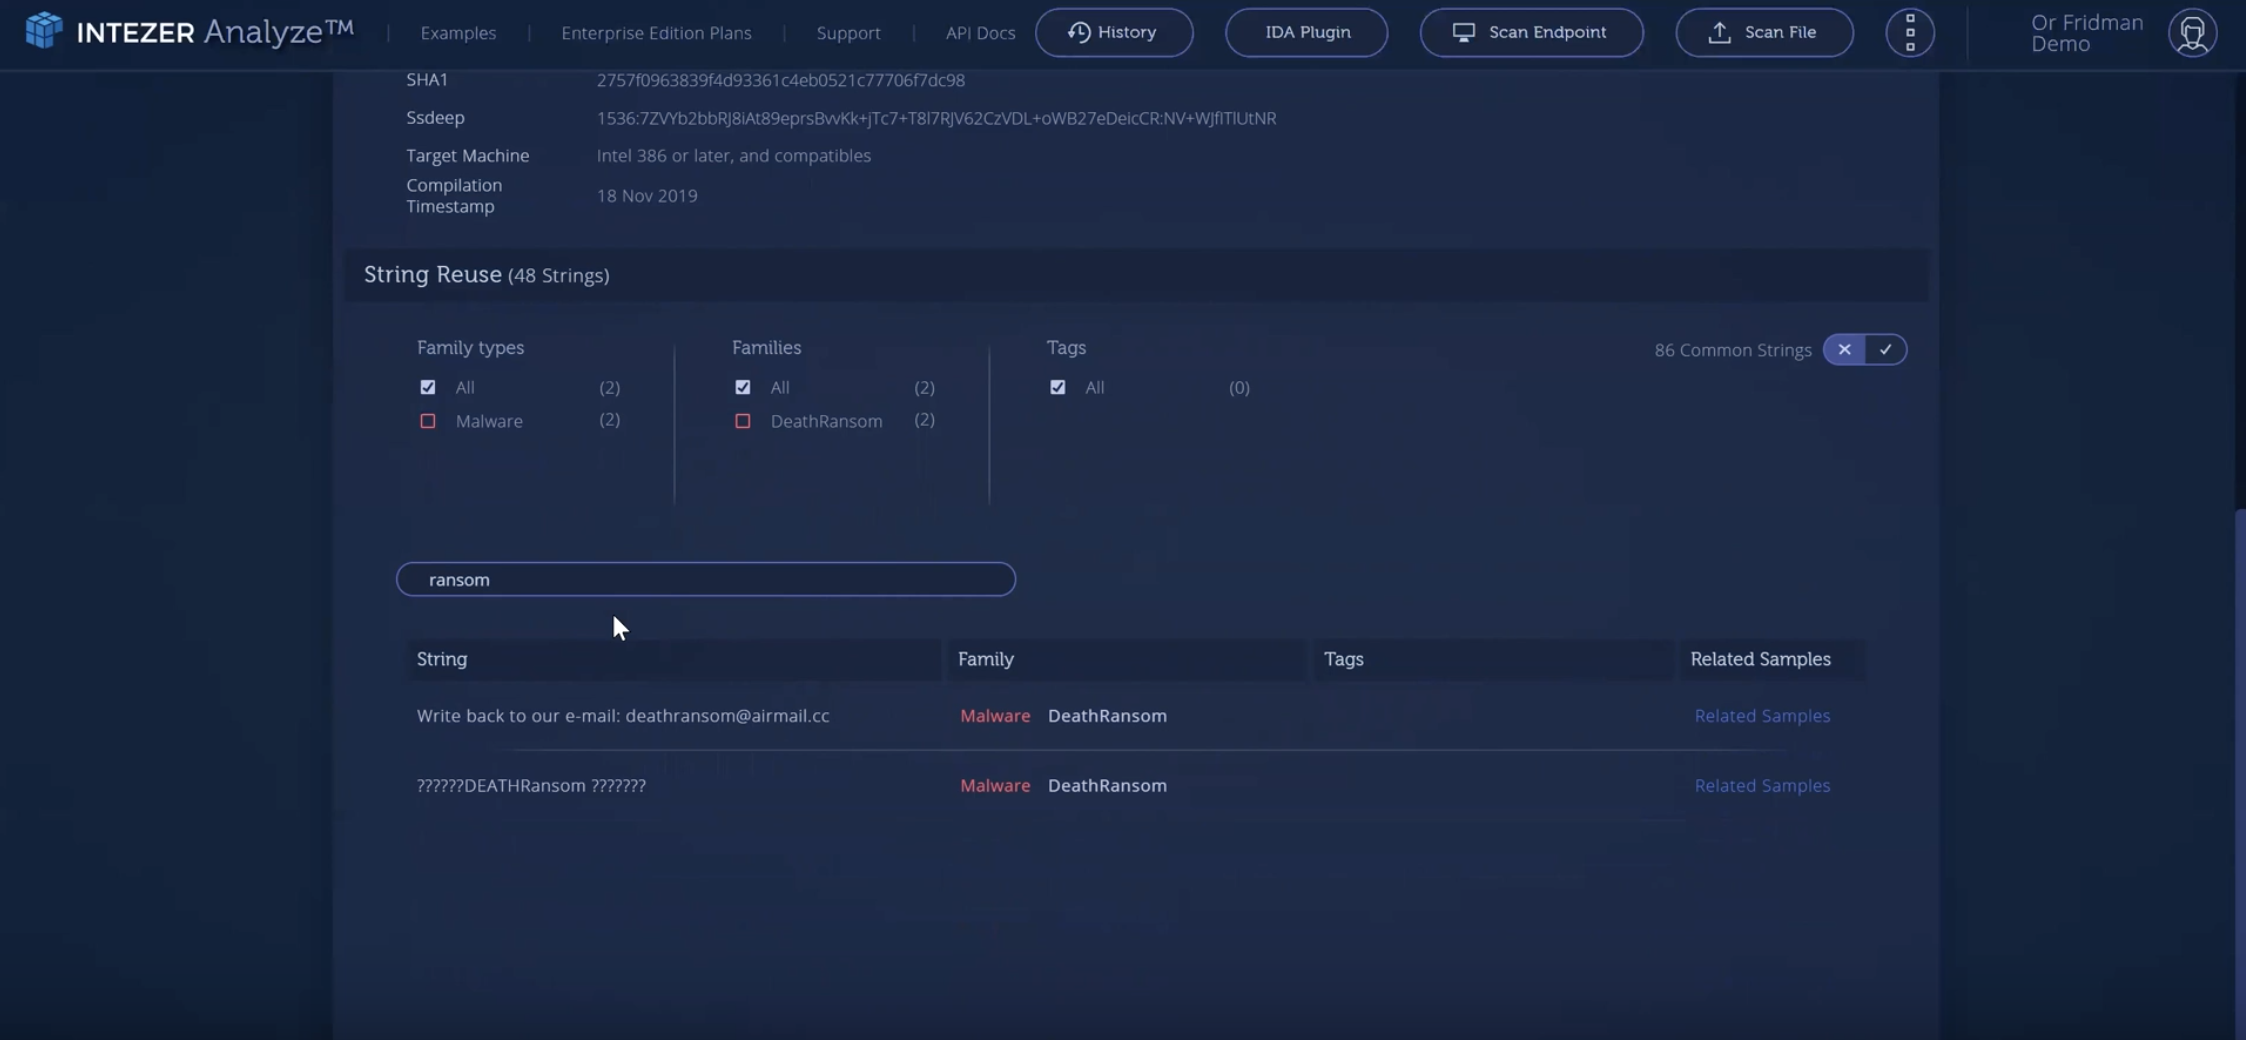
Search for revealing strings in Intezer Analyze
Accelerate your file investigations with new and improved string reuse capabilities in Intezer Analyze
Research
7 minutes
Fantastic payloads and where we find them
One of the most common anti-analysis tricks seen in today’s Windows malware is the use of packers. Packers often complicate the analysis and detection of binary files by hiding the malware’s real code and data; often referred to as the payload.
Malware Analysis
5 minutes
Evasion Techniques Dissected: A Mirai Case Study
To explain how code reuse analysis is different from signature-based detection approaches, let’s take a look at four Mirai samples which were recently uploaded to VirusTotal.

Malware Analysis
1 minute
Accelerate Reverse Engineering with Intezer Analyze IDA Pro Plugin
Reduce the analysis time from hours to minutes. Immediately focus on the relevant parts of the binary. See the plugin in action.
Incident Response
3 minutes
Ransomware and Spyware Top Intezer Analyze Community Detections
This month’s community highlights span a variety of file formats — APK, ELF and PE. Join the free Intezer Analyze community today.
Malware Analysis
2 minutes
Intezer Featured in IBM X-Force Threat Index
Drawing on previous IBM X-Force collaboration in detecting new malware variants, we used our Genetic Malware Analysis technology to measure malware innovation made by adversaries between 2018 and 2019. This measure of innovation is the extent to which threat actors invested in developing new code, suggesting that adversaries are looking to expand their threat capabilities and evade detection.
Research
8 minutes
New Iranian Campaign Tailored to US Companies Utilizes an Updated Toolset
We have discovered a new phishing campaign conducted by APT34. The Iranian-backed group is using an updated toolset tailored to US-based companies with the intent to evade detection.
Research
7 minutes
Linux Rekoobe Operating with New, Undetected Malware Samples
We have identified new variants of an old Linux malware known as Rekoobe, a minimalistic trojan with a complex CNC authentication protocol originally targeting SPARC and Intel x86, x86-64 systems in 2015.

Incident Response
4 minutes
Intezer Analyze Community: 2019 Recap and Trends
Incident Response
4 minutes
2019: A Year-in-Review
Research
10 minutes
ChinaZ Updates Toolkit by Introducing New, Undetected Malware
Incident Response
1 minute
Now Supporting Genetic Malware Analysis for Android Applications
Malware Analysis
4 minutes
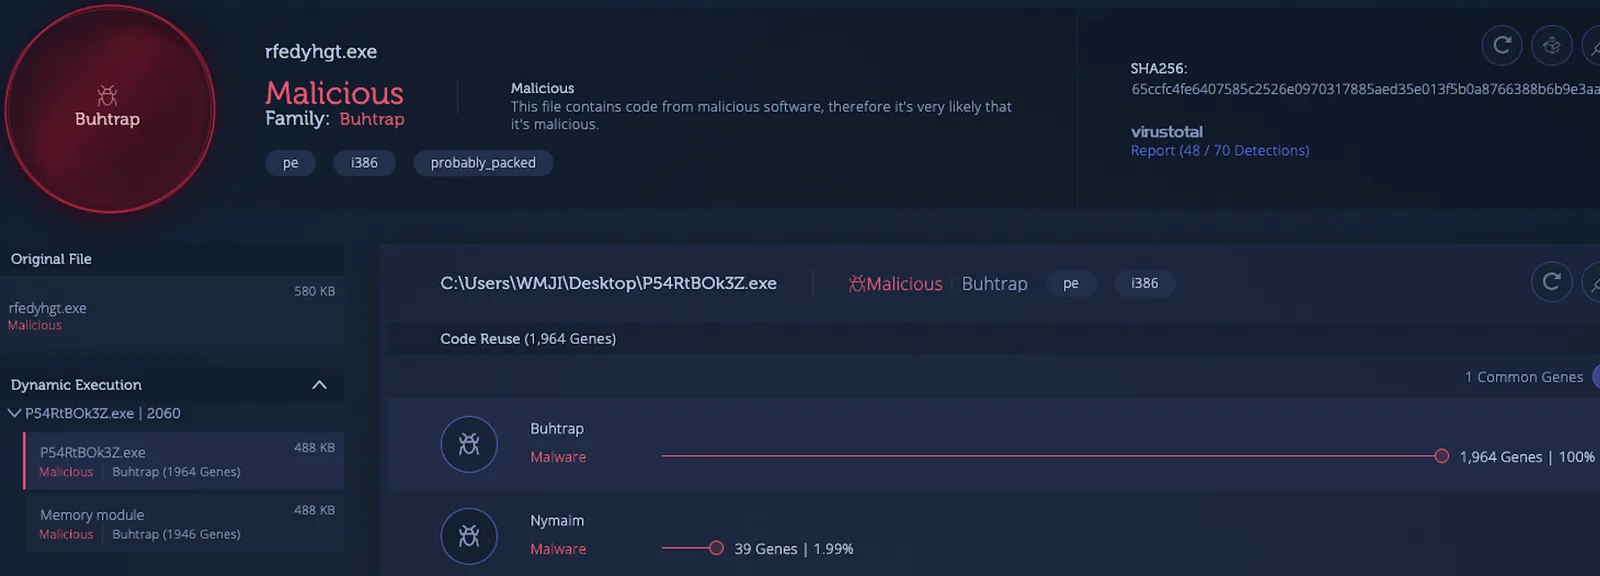
Intezer Analyze Community: Buhtrap, Divergent, Kronos, and More
November's community detections comprise a range of malware types, including banking trojans, exploit kits, and nation-state sponsored threats.