
Explore our blog
AI SOC
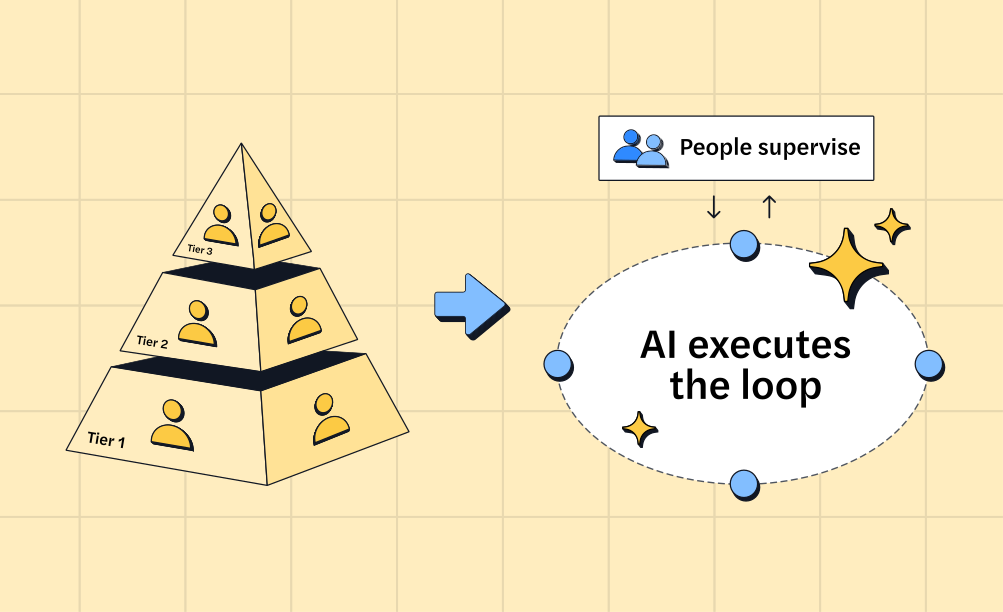
The end of the SOC pyramid
AI is retiring the SOC pyramid. Learn how a tierless AI SOC investigates 100% of alerts with forensic evidence while your analysts supervise outcomes.
Zev Schonberg
Research
5 min
NinjaMare and the enterprise security epidemic hiding behind a harmless label
The PUA label, aka "potentially unwanted application" means nuisance. Adware, toolbars, and other things that change your settings without asking. Our research team's findings say this label is far more serious than a mere nuisance.
Intezer
View Topics
Research
4 minutes
New Variants of Agent.BTZ/ComRAT Found: The Threat That Hit The Pentagon In 2008 Still Evolving; Part 1/2
Agent.BTZ–also known as ComRAT–is one of the world’s oldest known state-sponsored threats, mainly known for the 2008 Pentagon breach. Technically speaking, Agent.BTZ is a sophisticated user-mode RAT developed and operated by the Turla group in conjunction with Snake/Uroburos rootkit.
Research
4 minutes
“EternalMiner” Copycats exploiting SambaCry for cryptocurrency mining
About eight weeks ago, a critical RCE vulnerability present in every Samba version since 2010 was reported and patched. This vulnerability is mostly known as “SambaCry” after the famous WannaCry attack targeting Windows systems vulnerable to “EternalBlue” SMB exploit.
Incident Response
5 minutes
Without a Trace: The Dangers of Fileless Malware
Every day, wars are being waged on invisible battlefields. The enemy is hiding and stealthily leveling its attacks from within.
Incident Response
3 minutes
Introducing Cybersecurity DNA: the Intezer Company Blog
Have you ever searched for a needle in a haystack? In the world of cyber security, it might be that one problematic section or piece of code. Detecting cyber attacks certainly matters, but diagnosing them is also critically important.