
Explore our blog
AI SOC
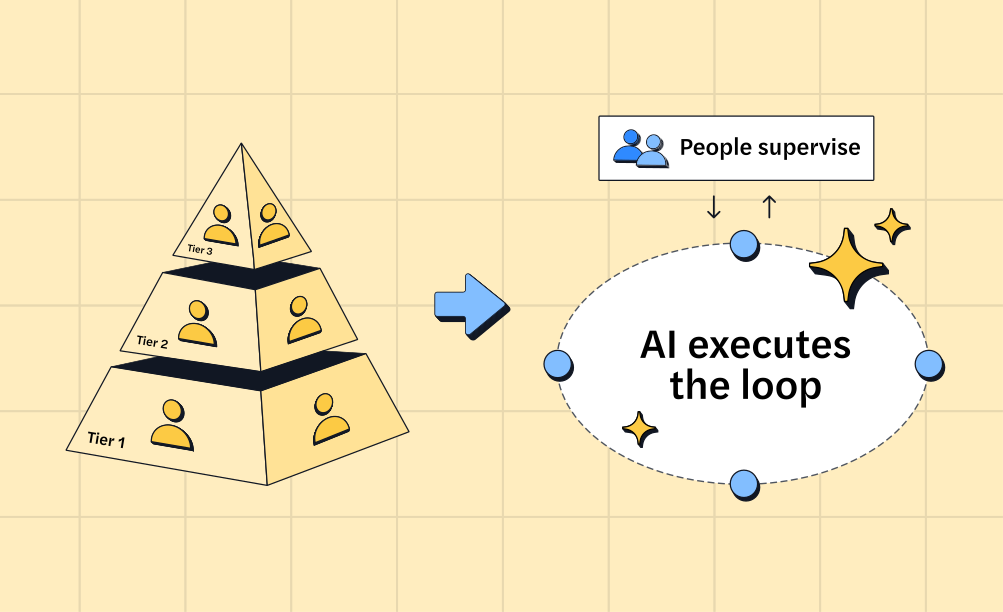
The end of the SOC pyramid
AI is retiring the SOC pyramid. Learn how a tierless AI SOC investigates 100% of alerts with forensic evidence while your analysts supervise outcomes.
Zev Schonberg
Research
5 min
NinjaMare and the enterprise security epidemic hiding behind a harmless label
The PUA label, aka "potentially unwanted application" means nuisance. Adware, toolbars, and other things that change your settings without asking. Our research team's findings say this label is far more serious than a mere nuisance.
Intezer
View Topics
Research
12 minutes
Babble Babble Babble Babble Babble Babble BabbleLoader
BabbleLoader: the annoyingly clever malware loader that jumbles, scrambles, and evades its way past modern defenses with frustrating ease.
Incident Response
4 minutes
How AI Can Help with Security Alert Correlation
Learn how AI-powered alert correlation improves security operations, enhances incident response, and reduces false positives.
Malware Analysis
26 minutes
Technical Analysis of a Novel IMEEX Framework

Incident Response
3 minutes
A $33M Investment to Extend SOC Teams’ Capacity
Intezer secures $33M to boost SOC teams with AI-driven automation, enhancing their capacity to handle alerts and prioritize critical threats.
Research
11 minutes
There's Something About CryptBot: Yet Another Silly Stealer (YASS)
In this blog, we analyze parallels and distinctions between two infostealers, underscoring why this new CryptBot variant demands attention.
Incident Response
25 minutes
How to Analyze Malicious MSI Installer Files
Learn about MSI installers and how threat actors use these files to evade security and execute malicious payloads in cyber attacks.
Research
11 minutes
Dissecting SSLoad Malware: A Comprehensive Technical Analysis
Learn about the stealthy SSLoad malware and its evolving nature, how it infiltrates systems, gathers reconnaissance, and delivers payloads.

Alert Triage
7 minutes
Mastering SOC Automation in 2024: Tips, Trends and Tools
Discover top tools and strategies for SOC automation—from AI co-pilots to Autonomous SOCs—and how to tackle alert overload and talent gaps.
Research
16 minutes
Memory Analysis 101: Understanding Memory Threats and Forensic Tools
Learn about memory forensics, its role in investigating security threats, how to analyze volatile memory and uncover malicious activities.
Incident Response
4 minutes
Examining Practical Use Cases for the AI-Powered SOC
Incident Response
3 minutes
MSSPs and MDRs Moving Fast to Adopt AI-Powered Automation
Explore how AI-driven automation helps MSSPs boost revenue, scale operations, and deliver high-quality cybersecurity outcomes for clients.
Alert Triage
7 minutes
The Ultimate Guide to CrowdStrike Falcon LogScale: A Next-Gen SIEM Showdown
Time to switch to a next-gen SIEM solution for log management? Let's breakdown the features and benefits of CrowdStrike Falcon LogScale.
Incident Response
24 minutes
.NET Malware 101: Analyzing the .NET Executable File Structure
This deep dive aims to guide you through .NET reverse engineering, equipping you with the essential knowledge to analyze .NET malware.

Incident Response
4 minutes
How Artificial Intelligence Powers the Autonomous SOC Platform
As cybersecurity teams look to leverage innovative AI-powered solutions, it's important to explain what "Autonomous SOC" means.
Incident Response
3 minutes
Interactive Browsing: A New Dimension to URL Analysis
After URLs get extracted and scanned, SOC analysts can use Interactive Browsing to securely explore and investigate malicious websites.