
Explore our blog
AI SOC
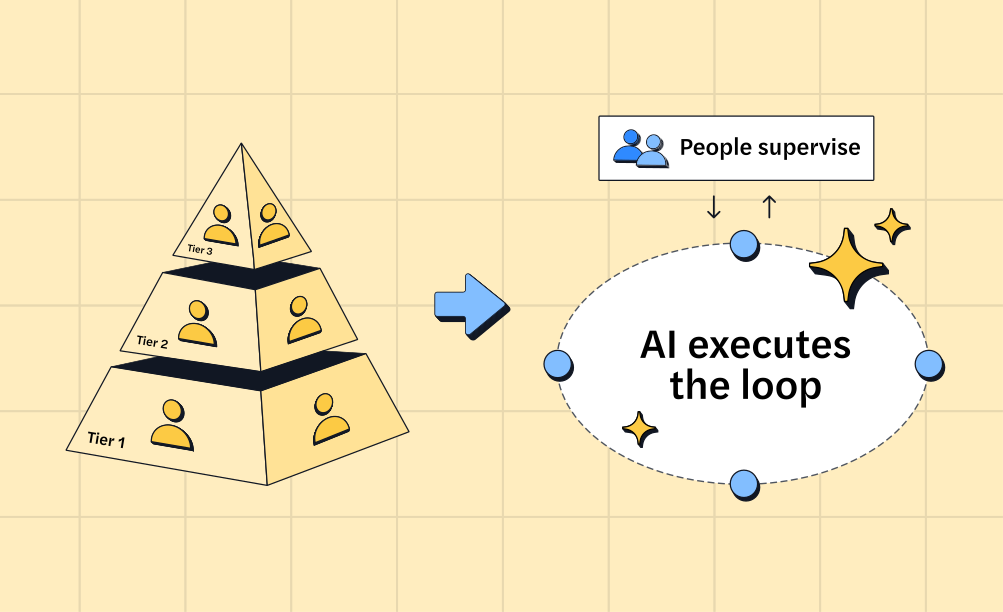
The end of the SOC pyramid
AI is retiring the SOC pyramid. Learn how a tierless AI SOC investigates 100% of alerts with forensic evidence while your analysts supervise outcomes.
Zev Schonberg
Research
5 min
NinjaMare and the enterprise security epidemic hiding behind a harmless label
The PUA label, aka "potentially unwanted application" means nuisance. Adware, toolbars, and other things that change your settings without asking. Our research team's findings say this label is far more serious than a mere nuisance.
Intezer
View Topics
Incident Response
3 minutes
Real Time Feedback: Fine-Tuning Autonomous SOC to Your Environment
The Autonomous SOC platform mimics the expertise of security analysts and uses your feedback to customize alert triage.
Incident Response
6 minutes
Speed Matters: The Crucial Role of MTTD and MTTR in Cybersecurity
Learn how MTTR and MTTD shape the cybersecurity landscape and new solutions like Intezer that can improve both metrics.
Incident Response
3 minutes
Automating Forensic Analysis for Linux Endpoints
Investigate Linux endpoints automatically, collecting and analyzing critical information with the new version of our endpoint scanner tool.

Incident Response
4 minutes
Growth of Autonomous SOC Platform Takes Off in 2023
Intezer’s Autonomous SOC Platform user base grew 400% in 2023—see real-world metrics, platform updates, and how AI automation is transforming security operations.
Research
16 minutes
Operation HamsaUpdate: A Sophisticated Campaign Delivering Wipers Puts Israeli Infrastructure at Risk
A sophisticated phishing campaign, with emails written in Hebrew, deploys a new wiper malware affecting Windows and Linux servers.
Incident Response
4 minutes
Threat Escalation: Focusing On What Matters Most
Threat escalation is critical for efficient incident response. Intezer investigates every alert, notifying you about confirmed, serious threats.

Incident Response
5 minutes
How MSSPs Use Smart Automation for Fast Incident Response
Here's 3 reasons top MSSPs are integrating advanced incident response automation to protect their clients from cyber attacks.
Research
13 minutes
WildCard: The APT Behind SysJoker Targets Critical Sectors in Israel
Our research team has identified a new APT group, dubbed "WildCard," initially detected through its use of the SysJoker malware.

Incident Response
10 minutes
What is Fileless Malware? Explained, with Examples
Discover how fileless malware works, why it’s hard to detect, and how to defend against in-memory threats.
Research
13 minutes
FBI Takedown: IPStorm Botnet Infrastructure Dismantled
UPDATE: The FBI has successfully secured a guilty plea from the individual responsible for the IPStorm infrastructure. Intezer's research team assisted in this case, sharing our findings and analysis about the new IPStorm malware variants and capabilities.
Incident Response
3 minutes
ServiceNow Security Operations: Streamlining Incident Response Workflows with Intezer
Discover how ServiceNow and Intezer streamline your security operations with smart decision making and comprehensive incident management.
Alert Triage
6 minutes
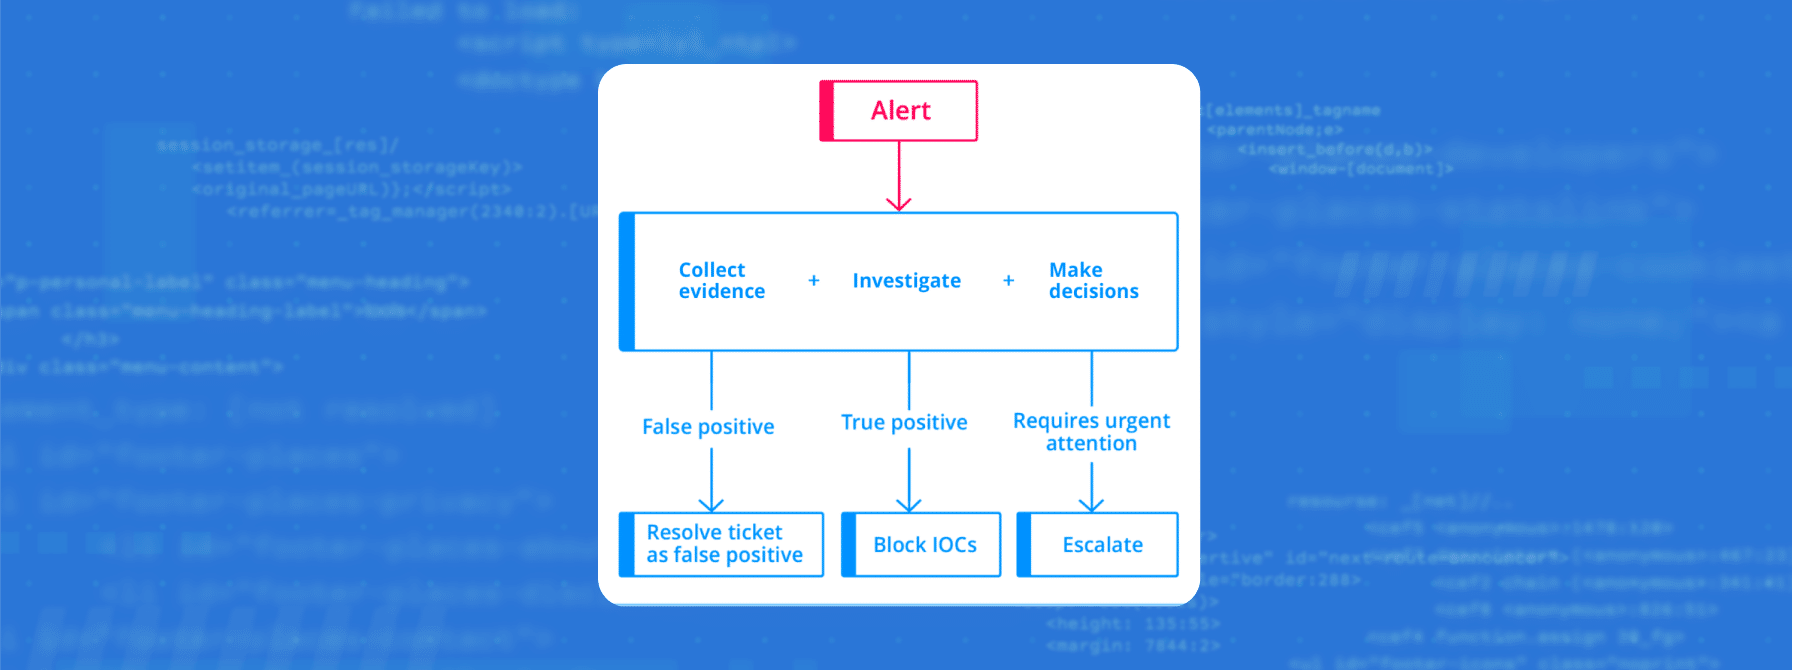
Supercharge These 3 Top Incident Response SOAR Playbooks
Make these three SOAR playbooks for cybersecurity response more effective, by combining AI decision-making with orchestrated actions.
Incident Response
16 minutes
Detect Phishing Emails by Inspecting Email Headers, Attachments, and URLs
Discover the top methods used by threat actors to deliver threats using phishing emails, as well as how to analyze the emails and attachments.
Incident Response
11 minutes
How to Analyze Malicious PDF Files
Here's how incident responders can use open-source and free tools to identify, detect, and analyze PDF files that deliver malware.
Incident Response
4 minutes
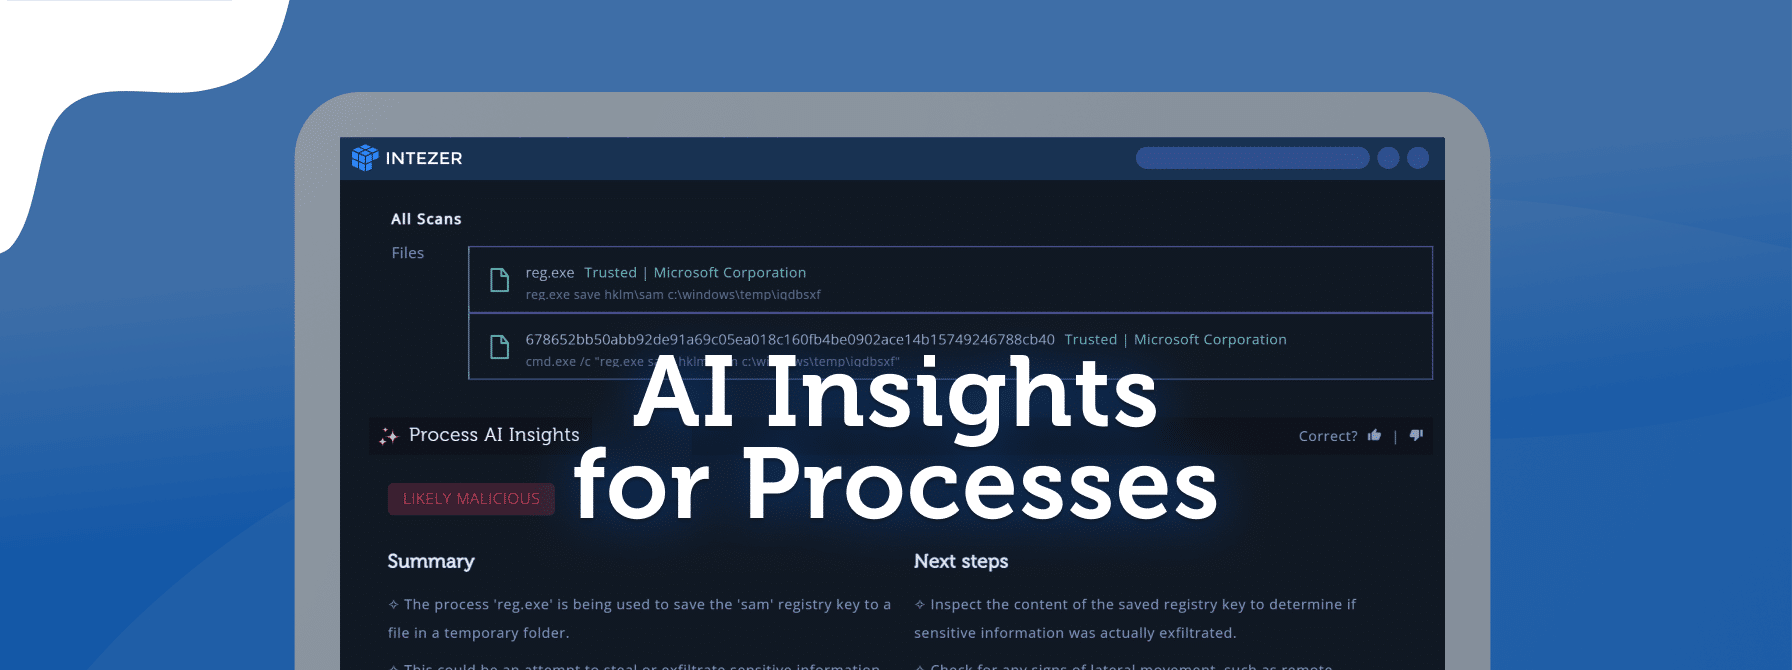
Introducing AI Insights for Processes: Triaging Command Lines and Other Text-Based Evidence
"Suspicious Activity" alerts are often ambiguous, especially when they involve PowerShell or command line processes. Intezer's AI Insights for Processes makes sure you have the answers you need while responding to these fileless alerts.