
Explore our blog
AI SOC
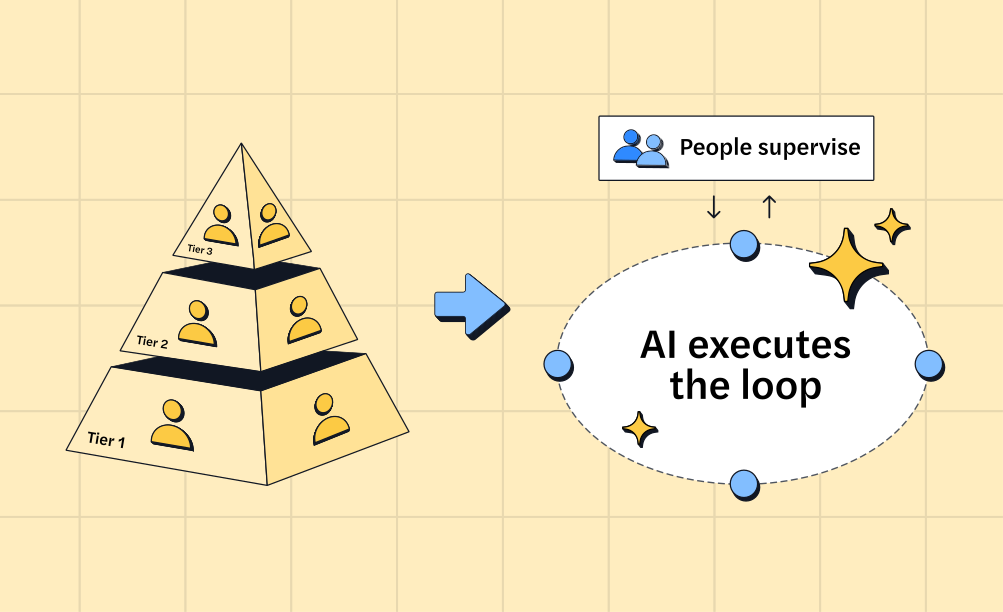
The end of the SOC pyramid
AI is retiring the SOC pyramid. Learn how a tierless AI SOC investigates 100% of alerts with forensic evidence while your analysts supervise outcomes.
Zev Schonberg
Research
5 min
NinjaMare and the enterprise security epidemic hiding behind a harmless label
The PUA label, aka "potentially unwanted application" means nuisance. Adware, toolbars, and other things that change your settings without asking. Our research team's findings say this label is far more serious than a mere nuisance.
Intezer
View Topics
Incident Response
4 minutes
Endpoint Forensics and Memory Analysis, Simplified
Here's how security teams can accelerate endpoint forensics to detect and analyze advanced in-memory threats like fileless malware.
Malware Analysis
8 minutes
How LNK Files Are Abused by Threat Actors
LNK files (aka Windows shortcuts) may seem simple, but threat actors can use them to execute other binaries and inflict great harm.
Alert Triage
5 minutes
Automating Alert Triage and Threat Hunting with SentinelOne + Intezer
To tackle the alert fatigue security teams experience and improve MTTR (mean time to respond), Intezer's integration with the SentinelOne Singularity XDR combines best of breed solutions to automatically triage incidents and provide advanced, enriched verdicts.

Incident Response
4 minutes
5 Key Factors for Selecting a Managed Detection and Response (MDR) Provider
There are a few things to look for when selecting an MDR provider that's right for you.
Incident Response
5 minutes
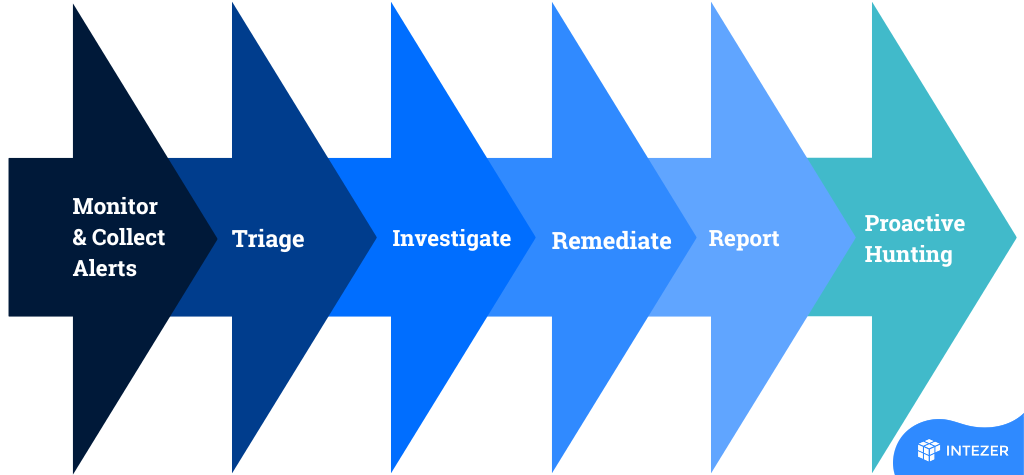
5 Reasons to Replace your Managed Detection and Response (MDR) Service
An MDR can help keep your business' cybersecurity up to date - but, there are a few reasons you'd want to consider replacing your MDR service.
Threat Hunting
5 minutes
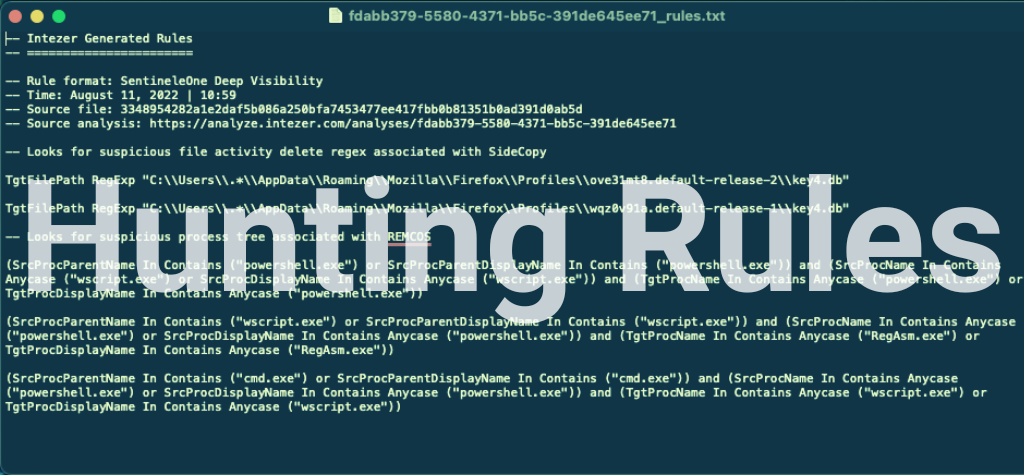
Threat Hunting Rule Extraction and Use Cases
Learn how to extract IOCs and behavioral indicators to a hunting rule format for your endpoint security system.
Alert Triage
6 minutes
CrowdStrike + Intezer: Automation for Alert Triage and Threat Hunting
Intezer’s solution for CrowdStrike functions as a virtual Tier 1, removing false positives and giving clear recommendations for every alert.
Alert Triage
2 minutes
macOS Threats: Automate Mac Alert Triage with Intezer
Automatically triage your security alerts about macOS files, processes, and endpoints by integrating with Intezer.
Threat Hunting
5 minutes
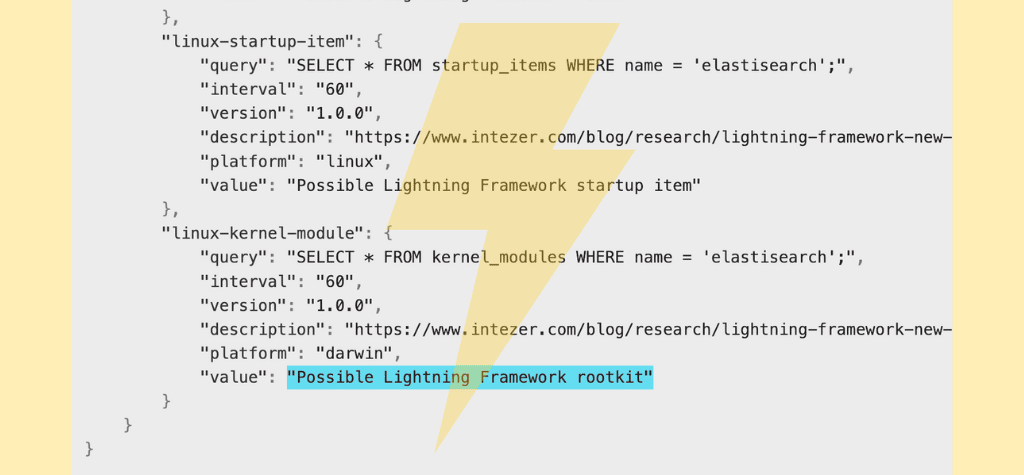
Detection Rules for Lightning Framework (and How to Make Them With Osquery)
Get hunting for traces of Lightning Framework, a new Linux threat, using this query pack we made with osquery.
Research
8 minutes
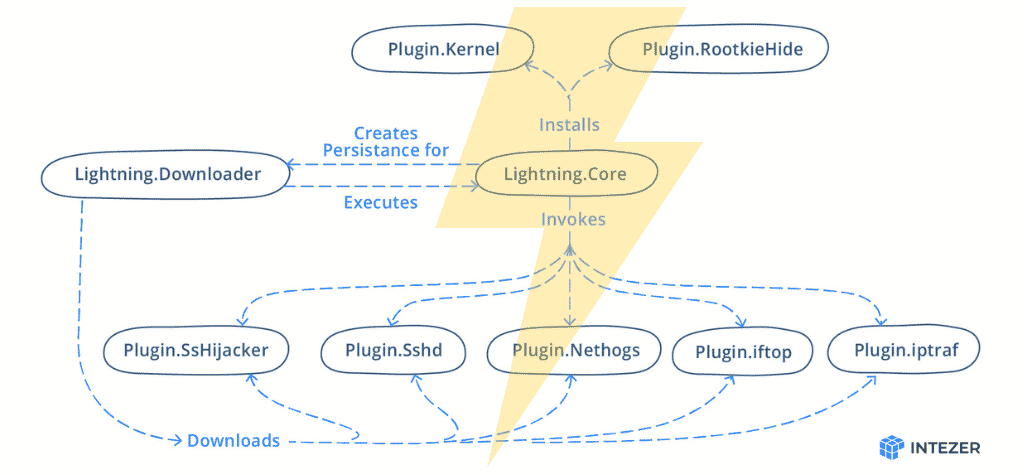
Lightning Framework: New Undetected “Swiss Army Knife” Linux Malware ⚡
A new Linux malware we're calling Lightning Framework has modular plugins and the ability to install multiple types of rootkits.
Incident Response
5 minutes
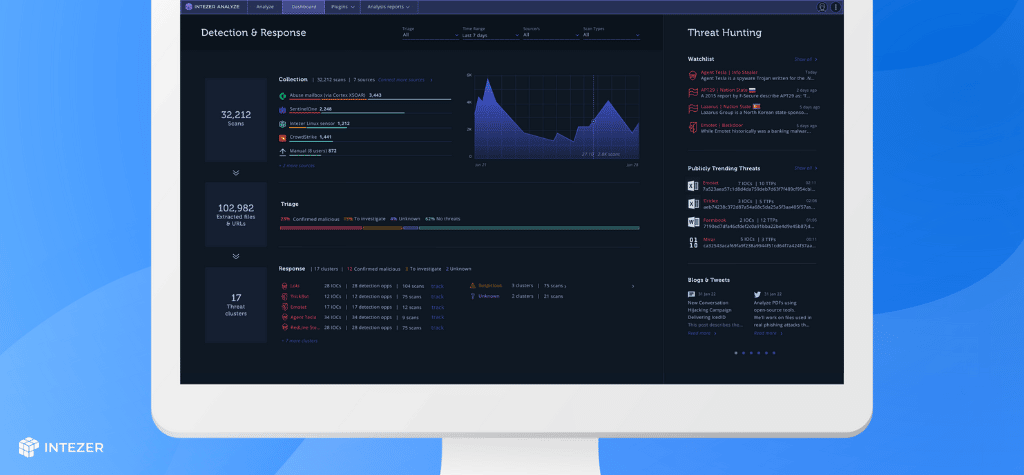
Autonomous SecOps: Your AI-Driven Tier 1 SOC Team
We are helping security teams go beyond individual file analysis to automate their entire Endpoint and Email alert triage processes with our new dashboard. Autonomous SecOps provides a better, more affordable alternative to in-house Tier 1 teams or external Managed Detection & Response services.
Research
13 minutes
OrBit: New Undetected Linux Threat Uses Unique Hijack of Execution Flow
OrBit is a new Linux malware that hijacks the execution flow, evading and gaining persistence to get remote access and steal information.
Research
9 minutes
YTStealer Malware: “YouTube Cookies! Om Nom Nom Nom”
YTStealer is a new malware we believe is sold as a service on the Dark Web for stealing authentication cookies from YouTube content creators.
Alert Triage
8 minutes
Needle in a Haystack: Analyzing Every Alert to Find Serious Threats
One of the greatest challenges SOC teams face is the high volume of daily alerts about suspicious files and endpoints to investigate.

Malware Analysis
2 minutes
Summary of Symbiote Research (A New, Nearly-Impossible-to-Detect Linux Threat)