
Explore our blog
AI SOC
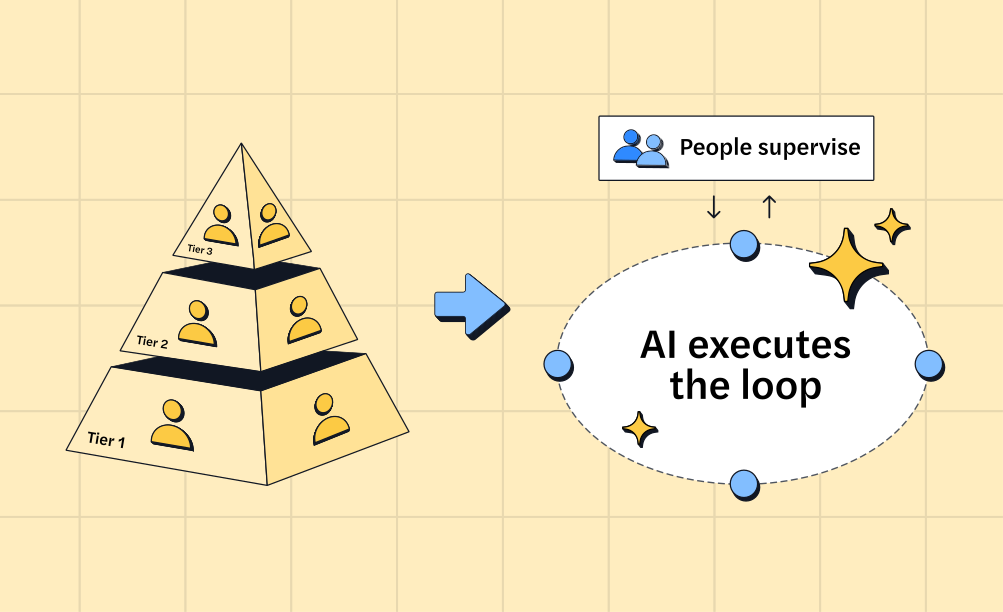
The end of the SOC pyramid
AI is retiring the SOC pyramid. Learn how a tierless AI SOC investigates 100% of alerts with forensic evidence while your analysts supervise outcomes.
Zev Schonberg
Research
5 min
NinjaMare and the enterprise security epidemic hiding behind a harmless label
The PUA label, aka "potentially unwanted application" means nuisance. Adware, toolbars, and other things that change your settings without asking. Our research team's findings say this label is far more serious than a mere nuisance.
Intezer
View Topics
Research
17 minutes
Symbiote Deep-Dive: Analysis of a New, Nearly-Impossible-to-Detect Linux Threat
Symbiote is a new Linux® malware we discovered that acts in a parasitic nature, infecting other running processes to inflict damage on machines.

Threat Hunting
3 minutes
Stay Ahead of the Latest Threats with Threat Family Tracking
Subscribe to threat actors/malware families in Intezer and receive notifications for new IoCs and detection opportunities.

Threat Hunting
10 minutes
SOC Level Up: Threat Hunting and Detection With Sigma
Sigma is a universal markup language for analyzing logs, which you can use to write threat hunting and detection rules for evolving threats.
Threat Hunting
9 minutes
How to Write YARA Rules That Minimize False Positives
Develop advanced YARA rules based on malicious code reuse, to increase the malware detection accuracy, reduce false positives, and improve your threat hunting.
Incident Response
7 minutes
Top Cyber Threats for the Telecom Industry to Watch in 2024
Incident Response
6 minutes
Top Cyber Threats to the Telecom Industry
Learn about top threats to the telecom industry and how teams are using automation to keep up with alert triage, incident response, and threat hunting.

Incident Response
6 minutes
Top Cyber Threats to the Manufacturing Sector
Manufacturers are building automated workflows for alert triage, incident response, and threat hunting to meet a rising volume of threats.

Alert Triage
5 minutes
Automate Alert Triage and Response Tasks with Intezer EDR Connect
Intezer EDR Connect gives you a simple way to automate alert triage tasks, by integrating with EDRs like CrowdStrike and SentinelOne.
Research
12 minutes
Elephant Framework Delivered in Phishing Attacks Against Ukrainian Organizations
Malware using the elephant malware framework was delivered via phishing emails from spoofed Ukrainian email addresses.
Incident Response
5 minutes
Security ROI: Time & Resource Savings for IR/SOC Teams
Automation can augment your security team to help you manage never-ending alerts, reduce skill gaps, and respond faster.
Research
8 minutes
New Conversation Hijacking Campaign Delivering IcedID
Intezer's research team has detected a new campaign which initiates attacks using conversation hijacking to deliver IcedID.

Threat Hunting
12 minutes
SOC Level Up: Introduction to Sigma Rules
SOC teams use Simga to write one rule that can be used across multiple environments. Learn how Sigma rules work and how to create them.
Threat Hunting
6 minutes
Scale Incident Response with Detection Engineering: Intezer Detect & Hunt
Cyber-attacks are on the rise and security teams are embracing an automation-first mindset using detection engineering to stay relevant. Intezer provides a solution for scaling incident response, the new Detect & Hunt feature in our enterprise edition.
Malware Analysis
6 minutes
How You Can Use Our New Open-Source Database Access Control Tool
Use this open-source Just-In-Time database access control tool (integrated with directory service, slack, and SIEM) to secure your database.
Incident Response
6 minutes
URL Analysis 101: Automating Phishing Investigations with Machine Learning
With a large volume of potentially malicious URLs, automated approaches like machine learning become critical.