
Explore our blog
AI SOC
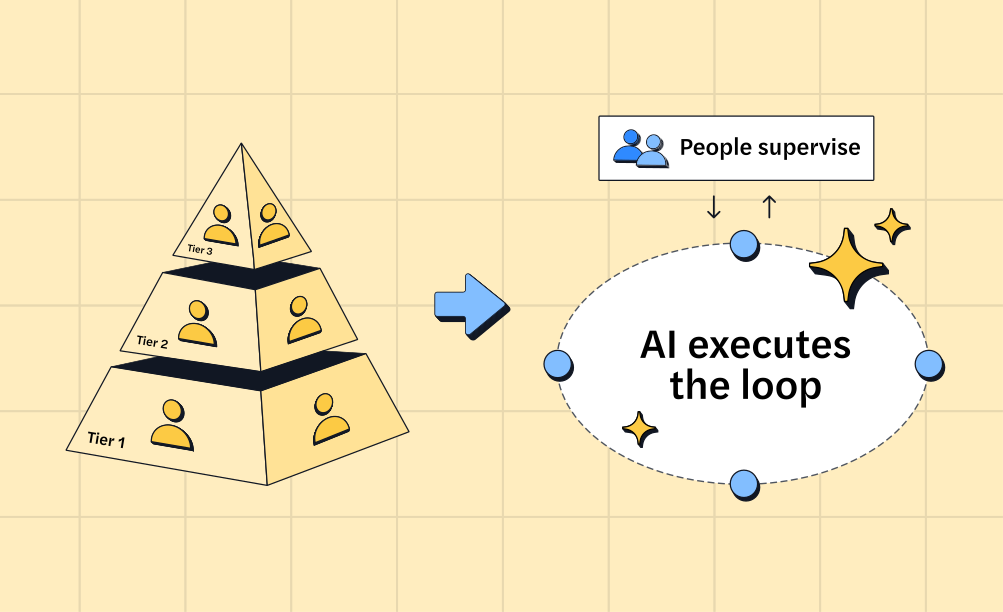
The end of the SOC pyramid
AI is retiring the SOC pyramid. Learn how a tierless AI SOC investigates 100% of alerts with forensic evidence while your analysts supervise outcomes.
Zev Schonberg
Research
5 min
NinjaMare and the enterprise security epidemic hiding behind a harmless label
The PUA label, aka "potentially unwanted application" means nuisance. Adware, toolbars, and other things that change your settings without asking. Our research team's findings say this label is far more serious than a mere nuisance.
Intezer
View Topics
Alert Triage
3 minutes
Intezer vs. MDR Service: Revolutionizing Alert Triage with Technology-Driven Efficiency
Unlike traditional MDR services and external SOCs, Intezer offers an advanced technology-driven solution for alert monitoring and triage.
Alert Triage
5 minutes
Intezer vs Sandbox: The Evolution from Sandbox to Comprehensive Automated Alert Triage
Intezer, an automated alert triage solution, offers a range of powerful analysis capabilities and existing security tool integration
Alert Triage
3 minutes
Automated, Context-Rich Alert Triage with AI Insights
Make investigations more effective with Intezer's automated evidence collection and analysis triaging alerts from your security tools.

Incident Response
3 minutes
Autonomous SOC Report: Enhance Transparency, Reduce Noise
Intezer sends you a weekly Autonomous SOC report with comprehensive insights into your alert pipeline, threat landscape, and recommendations to reduce noise.
Research
13 minutes
CryptoClippy is Evolving to Pilfer Even More Financial Data
New evidence indicates the CryptoClippy threat is evolving to target a broader range of payment services, beyond just crypto wallet theft.
Research
13 minutes
How Hackers Use Binary Padding to Outsmart Sandboxes and Infiltrate Your Systems
We've seen an uptick in threat actors using binary padding in an interesting way to evade defensive systems and sandboxes. So what is binary padding and how can you detect malware using this evasive technique?
Incident Response
5 minutes
Reducing Alert Fatigue in Your Security Operations Center with AI
Integrating AI Analysts as an extension of your security operations center can improve efficiency and boost the overall morale of your team.

Incident Response
4 minutes
Embracing AI Analysts to Strengthen In-House SecOps Teams
Can AI Analysts act like an extension of in-house SecOps teams, empowering human analysts to boost efficiency, scalability, and security?
Incident Response
4 minutes
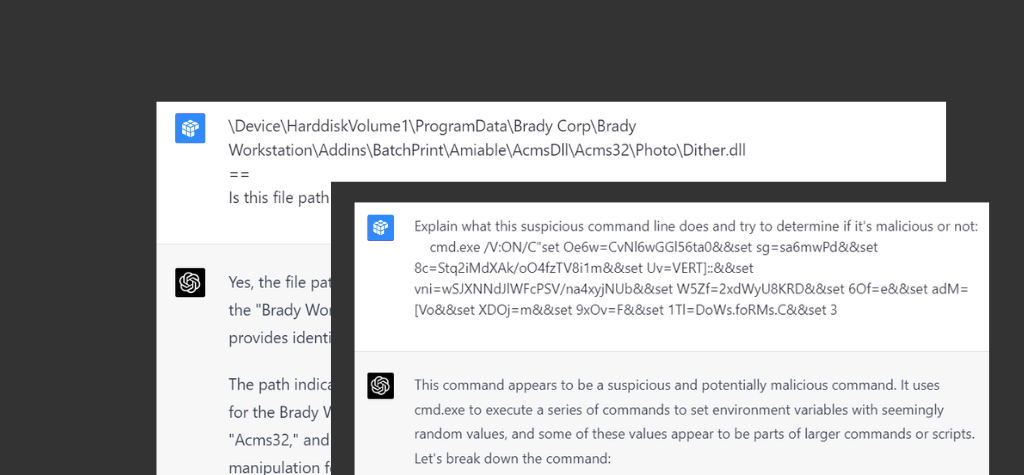
5 Ways to Use ChatGPT in Your SOC: Real-World AI Applications to Streamline Alert Triage
See how ChatGPT can assist your SOC team, with five practical ideas for using AI to streamline alert triage and cyber investigation tasks.
Research
8 minutes
Phishing Campaign Targets Chinese Nuclear Energy Industry
A phishing campaign with malicious payloads targeted the Chinese nuclear energy industry, using tactics that align with Bitter APT.
Incident Response
3 minutes
Infected: Understanding a Malicious Result from an Endpoint Scan
Got endpoint scan results about an infected machine? Know which details to pay attention to and how to use them for remediation.
Incident Response
3 minutes
Are Challenges Faced by SecOps Teams in 2023 an Opportunity?
SecOps teams face multiple challenges in 2023, forcing managers to rethink strategies and search for creative, scalable solutions.

Incident Response
11 minutes
Adopting AI-Powered Automation for Tierless SOC Teams
Manual security processes are no longer enough to keep up with the pace of threats, leading more organizations lean on SecOps automation.
Incident Response
12 minutes
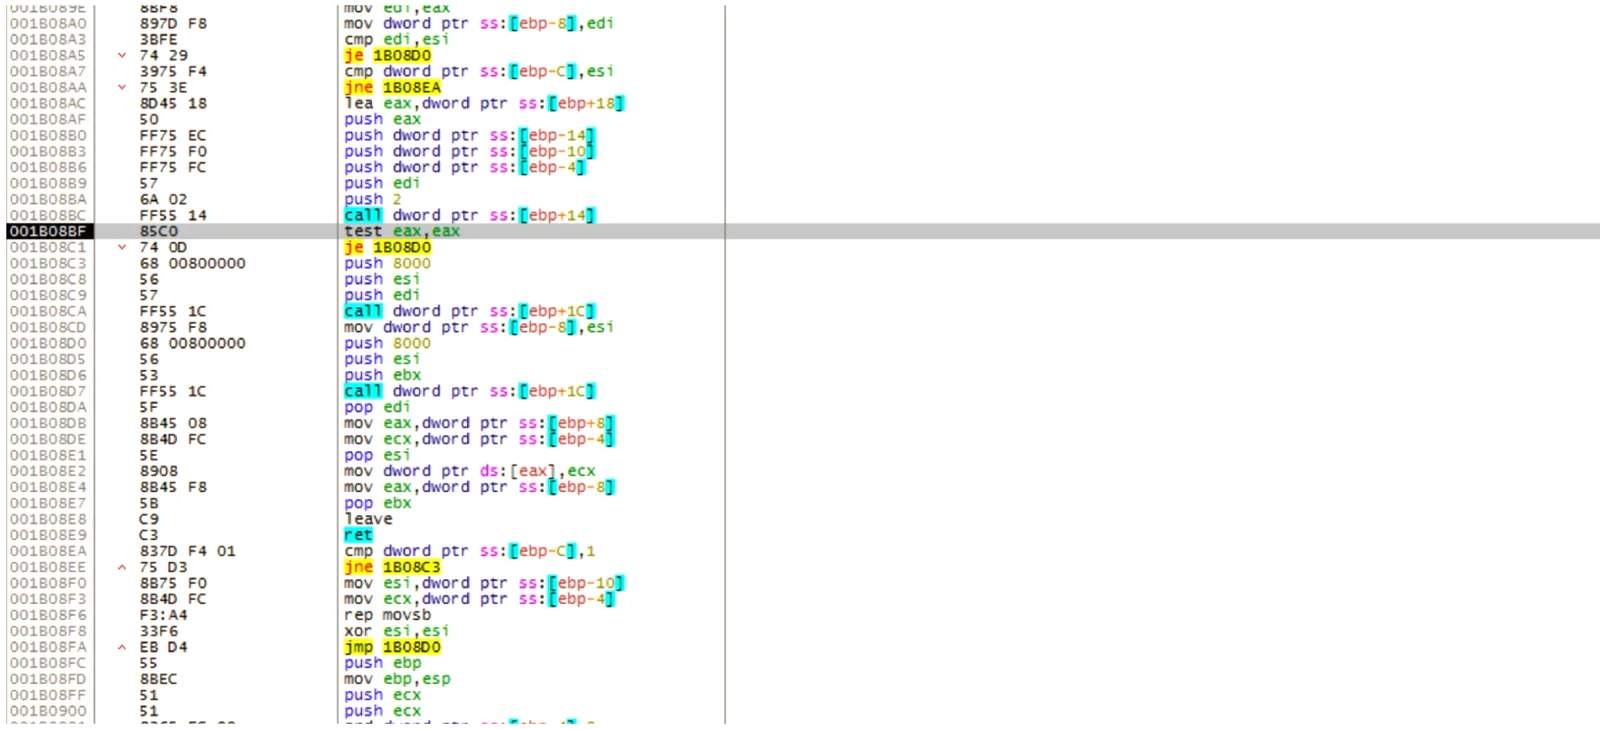
Malware Reverse Engineering for Beginners - Part 2
As a reverse engineer, you need to understand how malware is packed, obfuscated, delivered, and executed on the endpoint.
Incident Response
5 minutes
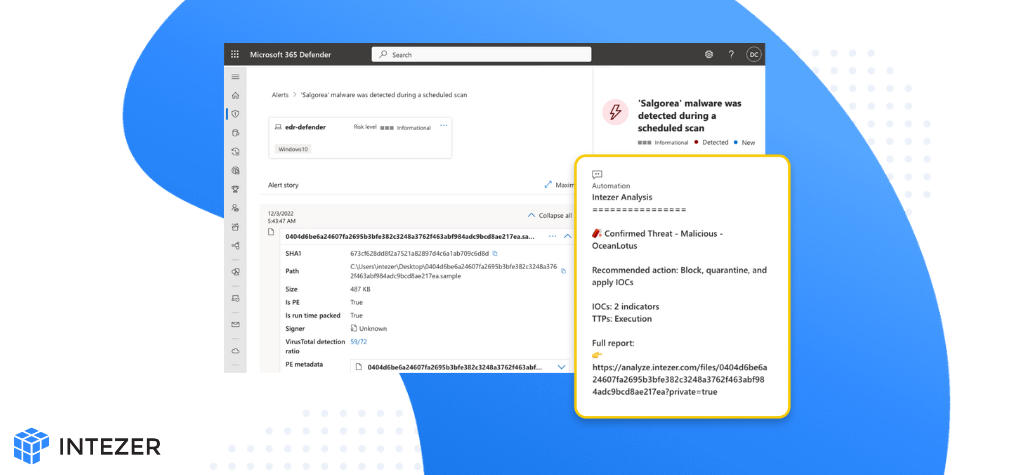
Scaling your SOC with Microsoft Defender + Intezer
Security teams can automatically triage incidents and get deep endpoint forensics by using Intezer’s Autonomous SOC solution with Microsoft Defender.