
Explore our blog
AI SOC
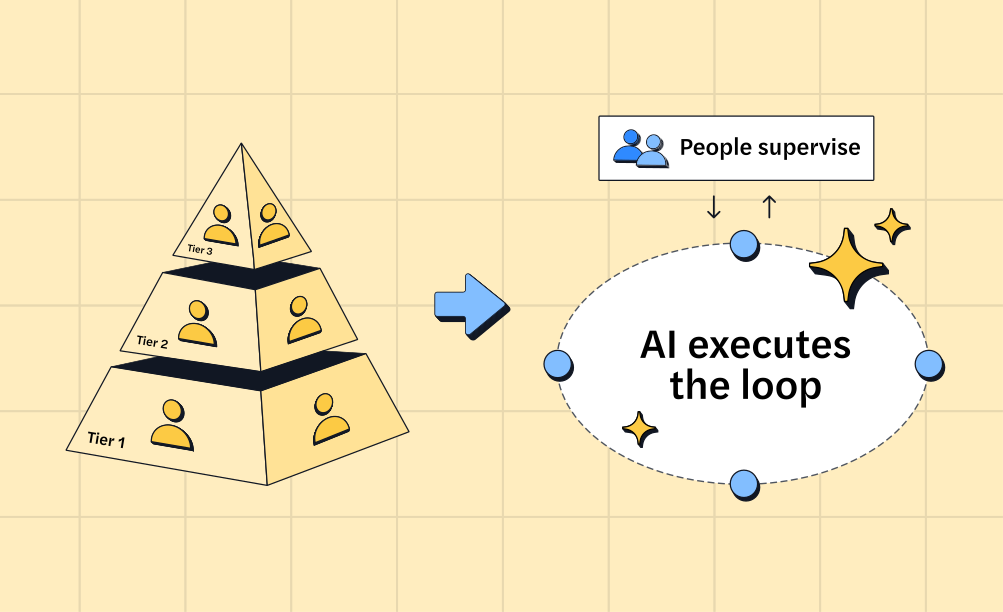
The end of the SOC pyramid
AI is retiring the SOC pyramid. Learn how a tierless AI SOC investigates 100% of alerts with forensic evidence while your analysts supervise outcomes.
Zev Schonberg
Research
5 min
NinjaMare and the enterprise security epidemic hiding behind a harmless label
The PUA label, aka "potentially unwanted application" means nuisance. Adware, toolbars, and other things that change your settings without asking. Our research team's findings say this label is far more serious than a mere nuisance.
Intezer
View Topics
Research
8 minutes
Boost Your SOC Skills: How to Detect Good Apps Gone Bad
Here's how to detect and trigger alerts when attackers are using trusted, legitimate tools in your environment for malicious purposes.
Incident Response
12 minutes
URL Analysis 101: A Beginner’s Guide to Phishing URLs
Learn about how to analyze suspicious URLs, by understanding URL structure and common manipulation techniques.
Malware Analysis
51 minutes
TeamTNT Cryptomining Explosion 🧨
TeamTNT is one of the most active cryptojacking actors targeting Linux servers. We trace a year of their campaigns, custom tooling and TTPs.
Alert Triage
4 minutes
Beyond Files: Automate URL Analysis with Intezer Analyze
URLs are common artifacts in suspicious emails and SOC alerts. Intezer Analyze scans suspicious URLs and dropped malware so you can quickly determine threats. Intezer Analyze has a public API, for integration with your phishing investigation pipelines.
Incident Response
2 minutes
Radare Plugin is Here for Intezer Community
When you're reverse engineering code as part of an incident response team, get information about threats faster with this Radare plugin.

Incident Response
5 minutes
4 Top Cyber Threats to the Finance and Insurance Industries
Cyberattackers follow the money. Read on to discover the top cyber threats for financial and insurance services seen in 2021.

Incident Response
8 minutes
3 Ways to Save Incident Response Time
Save time during incident response with these tips and tools to help your team accelerate HD, memory, and live forensics.

Cloud Security
10 minutes
Make your First Malware Honeypot in Under 20 Minutes
A honeypot is a powerful tool for threat intelligence. Collecting malware from attackers in a controlled environment helps stay one step ahead of stopping real attacks.
Threat Hunting
7 minutes
Detection Rules for Sysjoker (and How to Make Them With Osquery)
Using osquery to create detection rules for SysJoker can help you determine whether any of your systems are affected. SysJoker is otherwise undetected as Linux and macOS variants by any scanning engines on VirusTotal as of this publication.
Research
9 minutes
New SysJoker Backdoor Targets Windows, Linux, and macOS
In December 2021, we discovered a new multi-platform backdoor that targets Windows, Mac, and Linux that we have named SysJoker.
Malware Analysis
Research
11 minutes
Malware Reverse Engineering for Beginners - Part 1: From 0x0
Reverse engineering is an integral part of malware analysis and research - get started learning this advanced skill to investigate malware.

Malware Analysis
8 minutes
The Role of Malware Analysis in Cybersecurity
Security analysts use a variety of methods and tools to analyze suspicious files and endpoints in search of malware.
Malware Analysis
16 minutes
All Your Go Binaries are Belong to Us
Extract hidden metadata in binaries produced by the Go compiler and learn how it can be used to determine if an application uses a vulnerable dependency.
Malware Analysis
9 minutes
The State of Malware Analysis
Learn about malware analysis tools, their challenges, and what to look for when choosing the right solution.
Incident Response
10 minutes
New Type of Supply Chain Attack Could Put Popular Admin Tools at Risk
Registered retired usernames in GitHub could allow attackers to inject code into popular Golang projects and infect a large number of users.