
Explore our blog
AI SOC
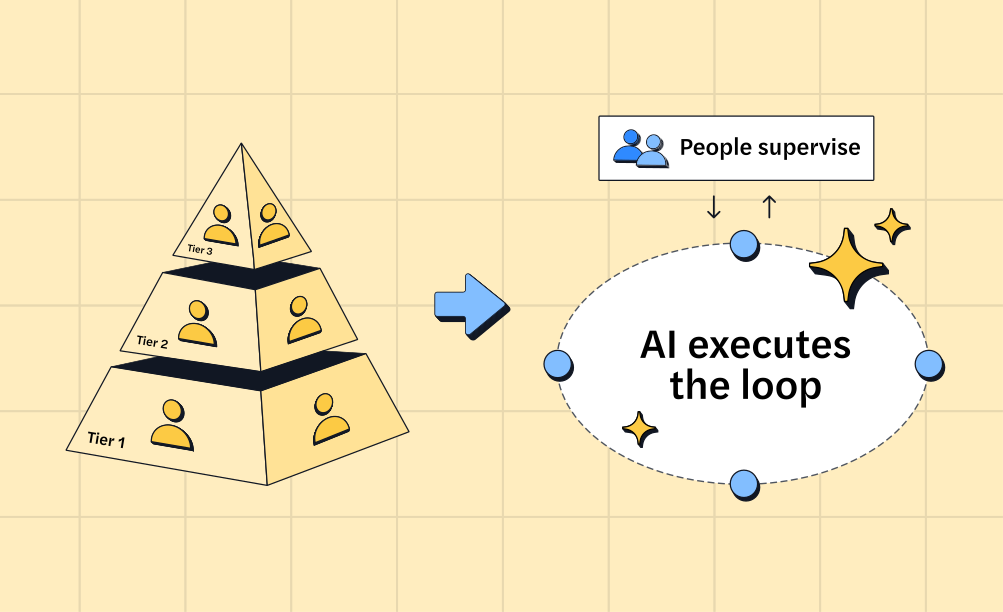
The end of the SOC pyramid
AI is retiring the SOC pyramid. Learn how a tierless AI SOC investigates 100% of alerts with forensic evidence while your analysts supervise outcomes.
Zev Schonberg
Research
5 min
NinjaMare and the enterprise security epidemic hiding behind a harmless label
The PUA label, aka "potentially unwanted application" means nuisance. Adware, toolbars, and other things that change your settings without asking. Our research team's findings say this label is far more serious than a mere nuisance.
Intezer
View Topics
Cloud Security
4 minutes
Conducting Digital Forensics Incident Response (DFIR) on an Infected GitLab Server
GitLab servers are under attack with a now-patched critical vulnerability.

Cloud Security
3 minutes
Exposed Prefect Workflows Could Lead to Disruptive Attacks
Hundreds of misconfigured Prefect instances could be the target of cyber attacks. Verify your instances are not exposed to the internet and enable MFA.
Cloud Security
11 minutes
Misconfigured Airflows Leak Thousands of Credentials from Popular Services
Misconfigured Apache Airflows expose credentials for popular services including Slack, PayPal and AWS. Airflow is the #1 rated open-source workflow project.
Cloud Security
9 minutes
Securing Microservices
There's a downside to microservices. When it comes to security, many of their benefits are potential weaknesses.
Incident Response
7 minutes
Teaching Capa New Tricks: Analyzing Capabilities in PE and ELF Files
When analyzing malware, one of the goals in addition to identifying what malware it is, is to understand what it does when it runs on a machine.
Malware Analysis
8 minutes
Vermilion Strike: Linux and Windows Re-implementation of Cobalt Strike
Vermilion Strike is a stealthy re-implementation of Cobalt Strike Beacon for Windows and Linux. Linux malware is fully undetected.
Research
2 minutes
Intezer Analyze Transforms for Maltego
With the Intezer Transforms, threat intel and SOC teams can quickly visualize malware classification and accelerate their investigations.
Malware Analysis
12 minutes
How to Detect Cobalt Strike
Learn about Cobalt Strike delivery mechanisms and how to detect them. Cobalt Strike is popular with threat actors since it's easy to deploy and use, plus its ability to avoid detection. Detect and analyze Cobalt Strike for free with Intezer Anlayze.
Malware Analysis
6 minutes
What MITRE D3FEND™ Techniques Does Intezer Analyze Implement?
Malware analysis platform, Intezer Analyze, implements key techniques from MITRE D3FEND™ including Script Execution Analysis and File Content Rules.
Cloud Security
13 minutes
Guide to Digital Forensics Incident Response in the Cloud
An increase in attacks on cloud infrastructure has led to the need for companies to develop strong security and incident response skills.
Malware Analysis
4 minutes
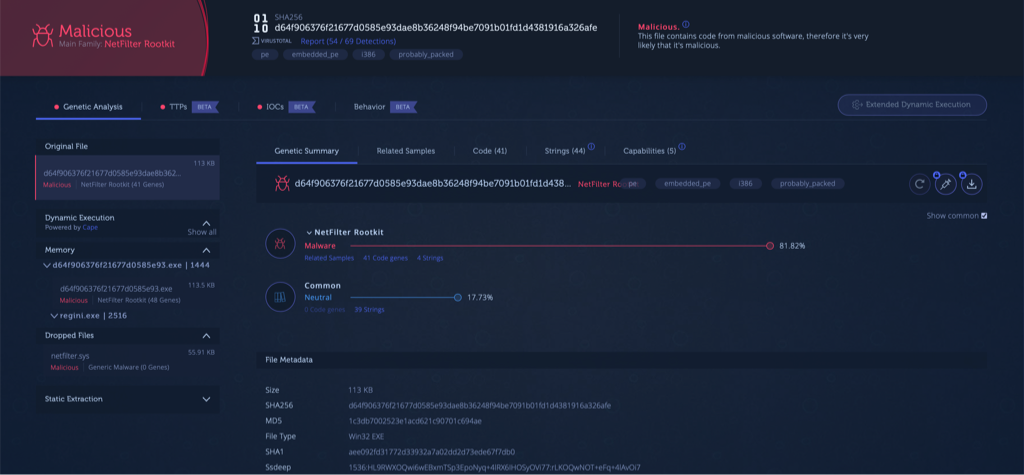
Fast Insights for a Microsoft-Signed Netfilter Rootkit
Get deep insights from a malicious Microsoft-signed Netfilter rootkit despite the valid signature.
Malware Analysis
4 minutes
Securing the Software Supply Chain
How to scope, plan, and execute an effective supply chain security initiative.
Cloud Security
5 minutes
New Attacks on Kubernetes via Misconfigured Argo Workflows
Attackers seen dropping cryptominers using this new method in the wild. Hundreds of exposed instances out there has the potential for large-scale attacks.
Malware Analysis
3 minutes
Reimagining the Malware Analysis Experience
Itai Tevet, CEO of Intezer, shares the company’s vision for a simplified, consolidated malware analysis experience.
Research
8 minutes
Targeted Phishing Attack against Ukrainian Government Expands to Georgia
Government agencies in Georgia targeted with an ongoing phishing attack. Intezer analyzed the latest samples.