
Explore our blog
AI SOC
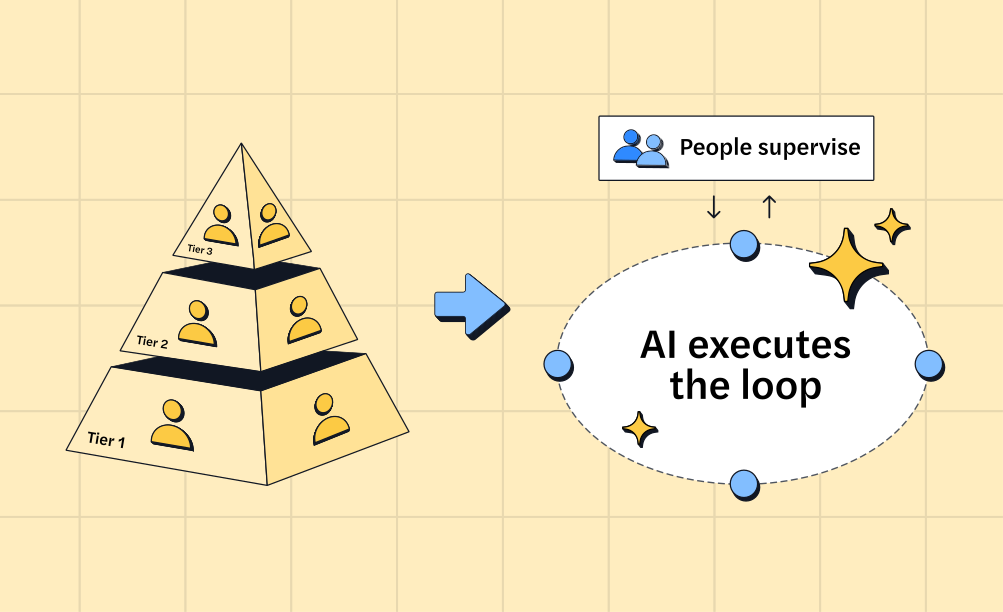
The end of the SOC pyramid
AI is retiring the SOC pyramid. Learn how a tierless AI SOC investigates 100% of alerts with forensic evidence while your analysts supervise outcomes.
Zev Schonberg
Research
5 min
NinjaMare and the enterprise security epidemic hiding behind a harmless label
The PUA label, aka "potentially unwanted application" means nuisance. Adware, toolbars, and other things that change your settings without asking. Our research team's findings say this label is far more serious than a mere nuisance.
Intezer
View Topics
Research
10 minutes
Energy Sector and its Suppliers Targeted in Global Phishing Campaign
A global phishing campaign is targeting energy, oil & gas suppliers, with attackers using typosquatted and spoofed phishing emails.

Malware Analysis
Research
4 minutes
Covering the Infection Chain: Analyze Documents and Scripts with Intezer Analyze
Investigate and classify non-executable files such as Microsoft Office documents, PDF files, and scripts such as PowerShell and VBS.
Malware Analysis
4 minutes
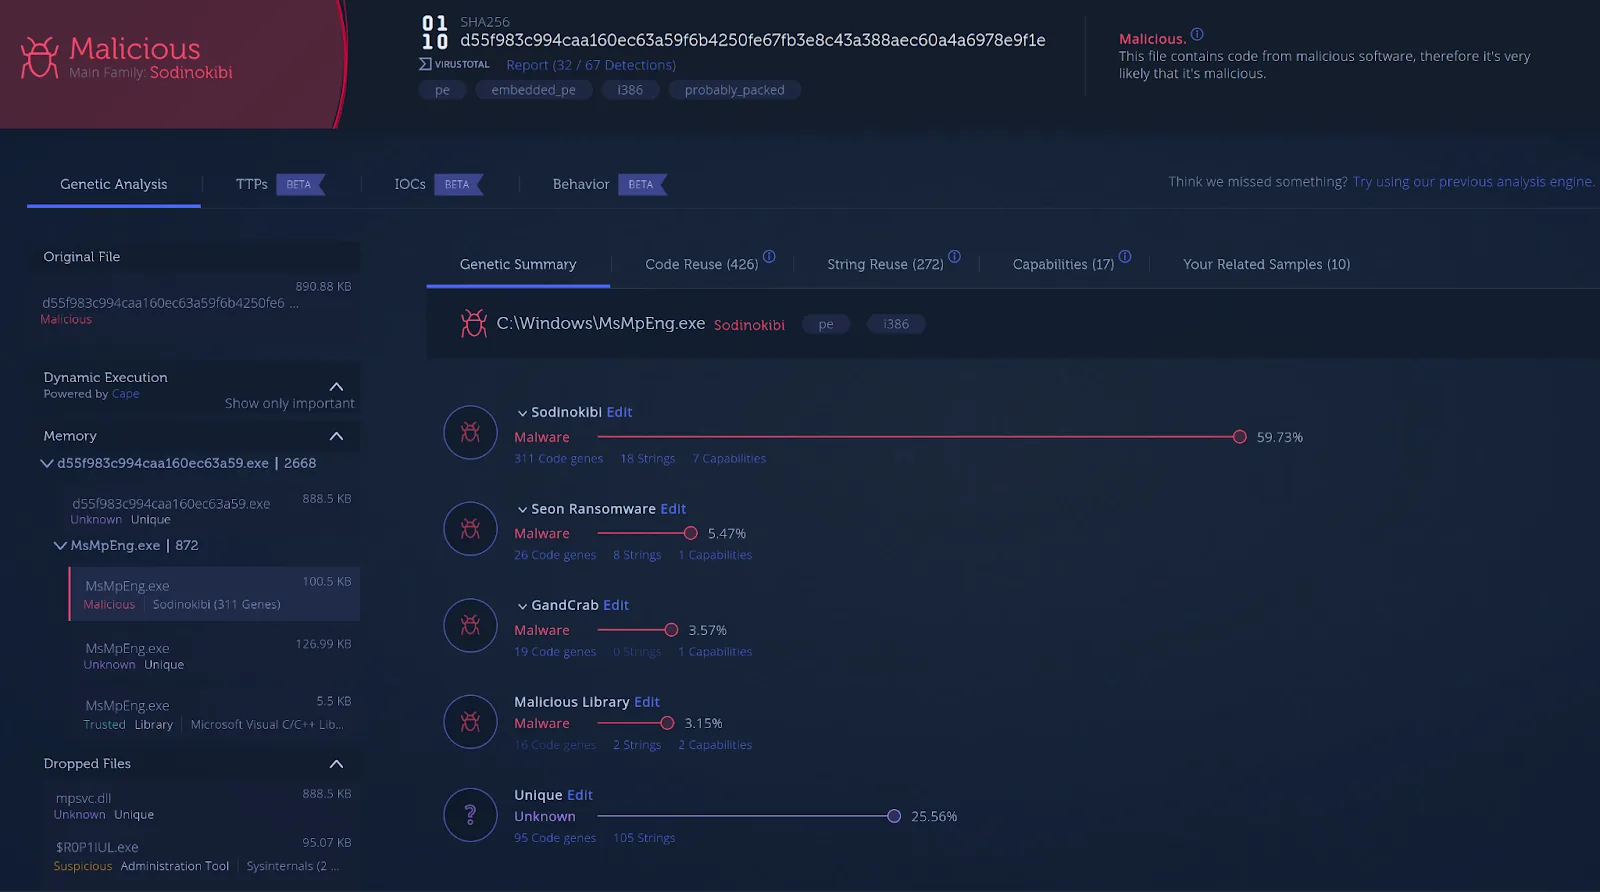
Genetic Analysis and Lessons Learned from REvil Attack
Validate your software supply chain for code tampering.
Malware Analysis
8 minutes
Klingon RAT Holding on for Dear Life
Intezer's technical analysis of an incredibly persistent Remote Access Trojan, Klingon RAT. The RAT is well-featured and resilient due to its multiple methods of persistence and privilege escalation. It is used by cyber criminals for financial gain.
Cloud Security
8 minutes
Top 10 Linux Server Hardening and Security Best Practices
As more companies adopt Linux, the frequency of Linux attacks is also increasing. These increased threats make hardening a worthwhile task.
Malware Analysis
7 minutes
Wrapping Up a Year of Infamous Bazar Campaigns
It has been 1 year since Bazar emerged on the cybercrime scene. We commemorate with key profiling and major milestones.

Cloud Security
6 minutes
Why Relying on the Cloud Provider for Security is Not Enough
The cloud providers offer built-in security tools designed to prevent a wide range of attacks. Yet, breaches still happen.
Cloud Security
6 minutes
CVE-2021-27075: Microsoft Azure Vulnerability Allows Privilege Escalation and Leak of Private Data
Vulnerability in Microsoft Azure VM Extension (CVE-2021-27075) would allow privilege escalation and leak of private data.
Malware Analysis
11 minutes
HabitsRAT Used to Target Linux and Windows Servers
Intezer has discovered a new malware variant, in addition to the version discovered by Shadowserver and Brian Krebs. The malware is written in GO and we are naming it HabitsRAT. It is targeting both Windows and Linux environments.
Cloud Security
5 minutes
How to Secure Cloud Non-Native Workloads
Not all applications are born cloud-native. Secure your cloud non-native workloads.

Cloud Security
5 minutes
Royal Flush: Privilege Escalation Vulnerability in Azure Functions
Disclosing a second Escalation of Privilege (EoP) vulnerability found in Azure Functions in the last few months.
Cloud Security
6 minutes
Rocke Group Actively Targeting the Cloud: Wants Your SSH Keys
Rocke Group is back with a new malware variant targeting the cloud. Check your system for compromise using these instructions.
Malware Analysis
3 minutes
Accelerate Incident Response with Intezer Analyze Volatility Plugin
Accelerate your incident response and memory forensics processes with the Intezer Analyze Volatility plugin.
Cloud Security
6 minutes
Top 10 Cloud Malware Threats
10 Linux malware targeting the cloud that should be on your radar.
Malware Analysis
Research
13 minutes
New Linux Backdoor RedXOR Likely Operated by Chinese Nation-State Actor
New backdoor targeting Linux systems likely attributed to China's Winnti Umbrella group.