
Explore our blog
AI SOC
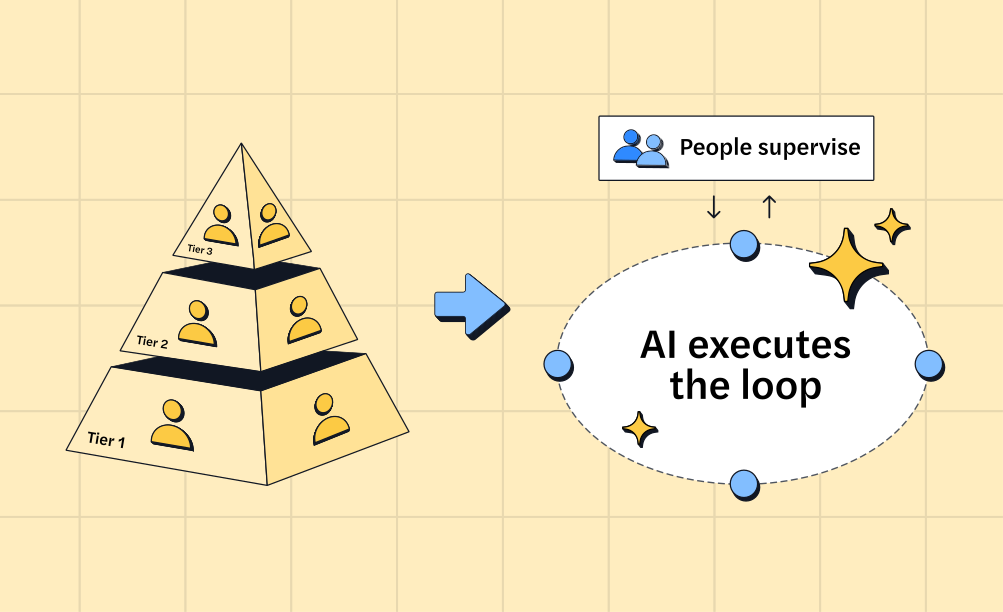
The end of the SOC pyramid
AI is retiring the SOC pyramid. Learn how a tierless AI SOC investigates 100% of alerts with forensic evidence while your analysts supervise outcomes.
Zev Schonberg
Research
5 min
NinjaMare and the enterprise security epidemic hiding behind a harmless label
The PUA label, aka "potentially unwanted application" means nuisance. Adware, toolbars, and other things that change your settings without asking. Our research team's findings say this label is far more serious than a mere nuisance.
Intezer
View Topics
Cloud Security
9 minutes
Watch Your Containers: Doki Infecting Docker Servers in the Cloud
Evidence shows it takes only a few hours from when a new misconfigured Docker server is online to become infected by this campaign.

Cloud Security
7 minutes
What is Zero Trust Execution? Definition, Adoption & More
Zero Trust Execution is a security approach that allows only pre-approved code to run in your cloud servers. It has become the industry recommended practice for securing cloud workloads.
Malware Analysis
4 minutes
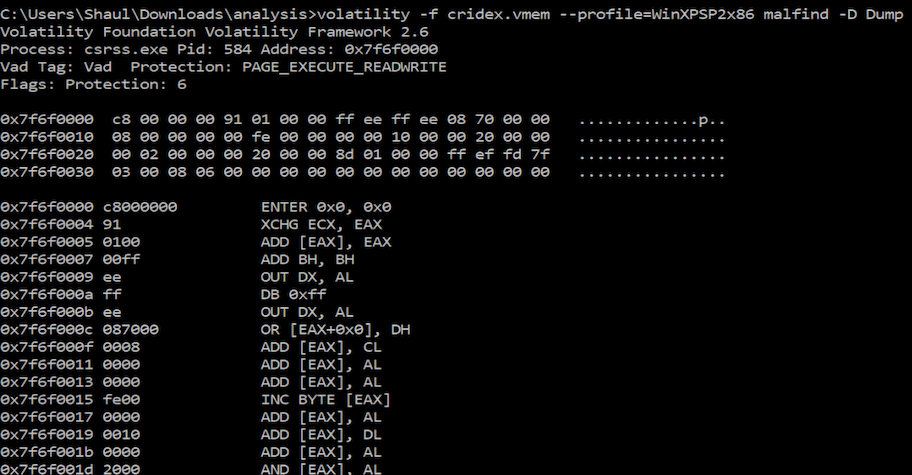
Accelerate Memory Forensics with Intezer Analyze
Accelerate the memory dump analysis process using the Volatility memory forensics framework and the Intezer Analyze CLI.
Cloud Security
8 minutes
Best Practices for Securing a Kubernetes Environment
Developing a new product with the help of a leading technology such as Kubernetes is a major investment. But without proper security measures in place, all that hard work can go to waste.
Malware Analysis
1 minute
Community Ghidra Plugin is Here
Accelerate reverse engineering with the Intezer Analyze Ghidra plugin. Get the plugin from our GitHub repository.
Malware Analysis
2 minutes
Detect Malware Associated with the Most Exploited CVEs
Last month, the US-CERT urged IT security professionals to patch the most common vulnerabilities exploited by foreign cyber actors from 2016 to 2019.
Malware Analysis
1 minute
IDA Pro Plugin Now Available to the Community
Accelerate reverse engineering by enriching every function of disassembled machine code with info about where the code was seen previously.
Cloud Security
6 minutes
Best Practices for Securing a Docker Runtime Environment
This article lays out a checklist of Docker security best practices, starting with the development phase, continuing on to deployment, and finally the runtime environment.
Malware Analysis
8 minutes
ELF Malware Analysis 101: Linux Threats No Longer an Afterthought
Practice ELF malware analysis hands-on. Attackers have targeted the Linux OS aggressively in recent years.
Malware Analysis
2 minutes
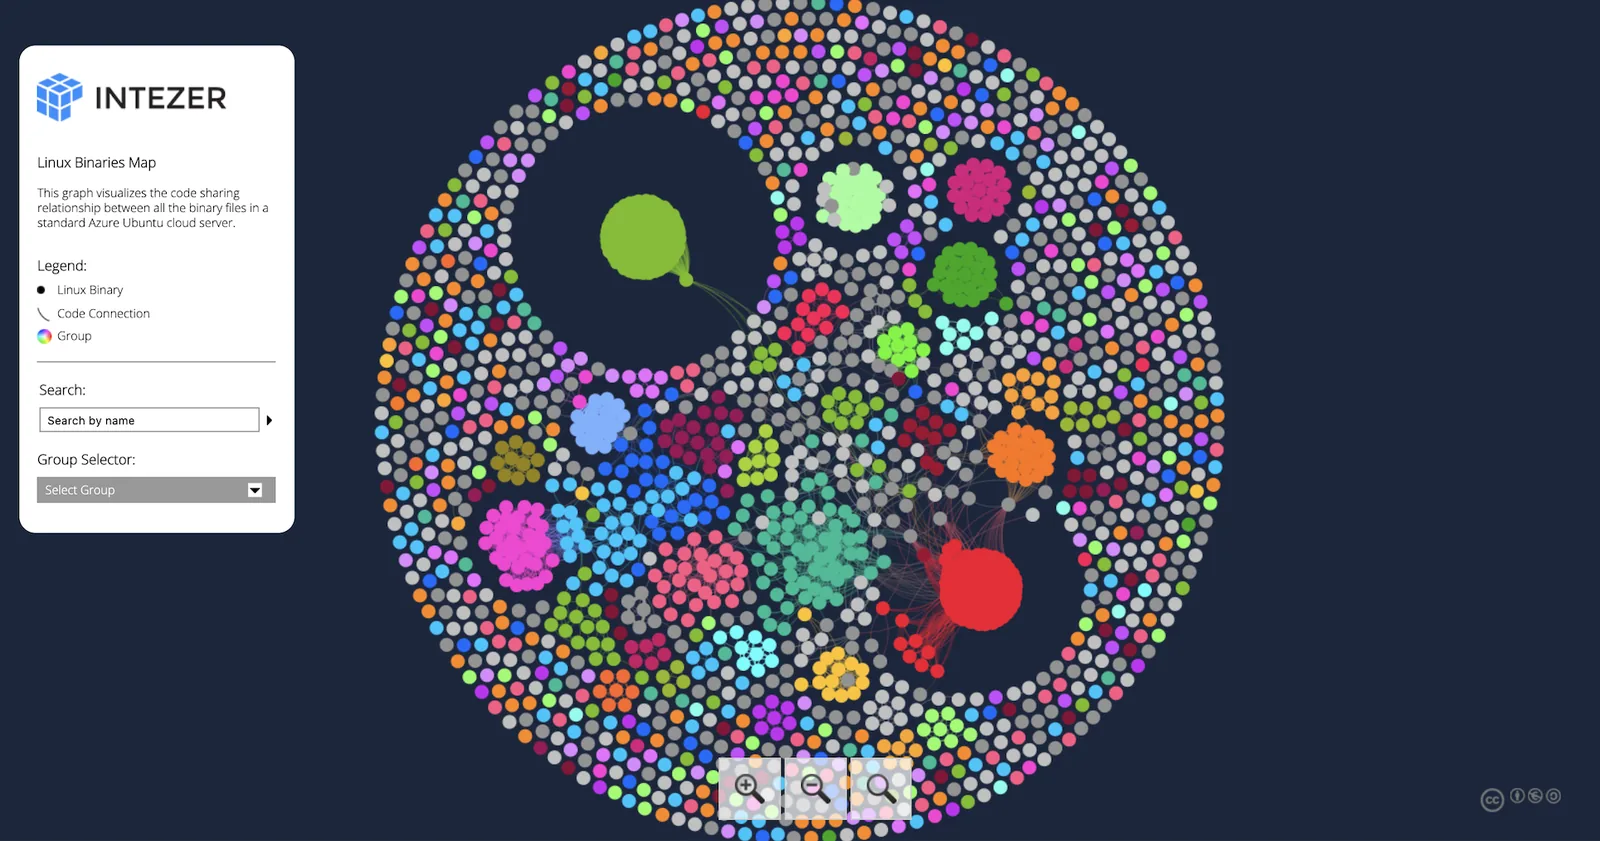
Mapping Binaries Inside a Microsoft Azure Cloud Server
This interactive map allows you to explore the code sharing relationship between all binary files in a standard Azure Ubuntu cloud server.

Research
6 minutes
The Evolution of APT15’s Codebase 2020
The Ke3chang group continues to alter its code and substitute basic functionalities in its backdoors.
Cloud Security
3 minutes
Exploitation of SaltStack Vulnerabilities Signals Increase in Cloud Server Attacks
The recent exploitation of SaltStack vulnerabilities signals an increase in cloud server attacks.
Research
5 minutes
Kaiji: New Chinese Linux malware turning to Golang
Kaiji—a new Chinese malware targeting servers and IoT devices with a custom implant—is part of a greater threat actor migration to Golang.
Malware Analysis
1 minute
Intezer Analyze community roundup
Maze ransomware and APT41 highlight this month's community samples. Join the free Intezer Analyze community to detect malicious software in seconds.

Malware Analysis
2 minutes
Malicious APKs share code during Covid-19 pandemic
-1331